Author: zeraconsulting

  • Enterprise n8n: 6 Step Service Principal Setup for Microsoft 365

    Enterprise n8n: 6 Step Service Principal Setup for Microsoft 365

    Yes, n8n handles Microsoft 365 integration well, and for most mid-market firms it should sit alongside Copilot and Power Automate rather than replace them. For production workflows, register a Microsoft Entra Service Principal (app-only) credential instead of OAuth2 delegated auth. Grant the required Graph application permissions, get admin consent, then wire up the n8n credential and run the test call before building anything else.


    TL;DR:

    • Using a Service Principal is essential for unattended, scheduled, or shared workflows in Microsoft 365, as it ensures persistent and permissioned access.
    • Most failures stem from missing admin consent or incorrect Graph API permission assignments, which are often fixed by granting admin approval and checking required scopes.
    • Building automation patterns like invoice alerts or client onboarding requires testing on sandbox tenants and careful permission management for secure, reliable operation.
    • The Microsoft Graph API base URL must match the tenant type (global, US government, DOD, China) to prevent silent call failures in production.
    • Regularly rotating secrets or using certificates enhances security, with certificates offering longer lifecycle benefits over secrets and integration with existing secrets management systems.

    Gozera
    Turn Automation Into Measurable ROI
    Zera helps professional-services firms integrate tailored workflows, measure usage, and optimize Microsoft 365 Copilot for tangible business value.

    Explore Zera’s approach

    Table of Contents

    Which Microsoft 365 Nodes Does n8n Support?

    n8n ships native nodes for the Microsoft 365 apps that professional-services firms actually run their operations on. Each node exposes multiple operations, and the credential you attach determines what those operations can actually touch.

    The core set includes:

    • Microsoft Teams node — send channel messages, create channels, manage members, and post adaptive cards, per the Teams node documentation.
    • Microsoft Outlook node — create and send drafts, manage calendar events, and handle attachments, with three credential options including Service Principal, according to the Outlook node docs.
    • Microsoft Excel 365 node — read and write worksheet rows, useful for time-entry aggregation or invoice logs.
    • Microsoft OneDrive node — upload, move, and share client deliverables programmatically.
    • Microsoft To Do node — create and update tasks tied to intake or onboarding checklists.

    A common pattern: an Outlook trigger catches a new client intake email, an Excel node logs the request, and a Teams node notifies the account lead. Under app-only credentials, some user-context operations (like reading a specific mailbox folder structure tied to a signed-in user) are limited, so map your use case to Graph application permissions before you build.

    Should You Use Service Principal or OAuth2 for Microsoft 365 Auth?

    The decision comes down to who is running the workflow and how long it needs to survive unattended. If a human triggers the flow and stays logged in, OAuth2 delegated auth works fine for a proof of concept. If the workflow runs on a schedule, processes shared mailboxes, or posts to Teams without anyone watching, use a Microsoft Entra Service Principal. There is no signed-in user to expire, which is exactly why the n8n documentation on Service Principal credentials recommends it for unattended, shared workflows.

    Here is the setup sequence for production-grade app-only auth:

    1. Register a new application in Microsoft Entra ID (App registrations).
    2. Add the Microsoft Graph application permissions your workflow needs (covered node-by-node below).
    3. Generate a client secret or, for stricter security postures, upload a certificate instead.
    4. Confirm the Graph API Base URL matches your tenant type (Global, US Government, US Government DOD, or China), since n8n’s Microsoft credentials support all four environments.
    5. Grant admin consent for the permissions in the Entra admin center. This step gets skipped constantly and is the number one cause of failed credential tests.
    6. Create the matching credential in n8n and run the built‑in credential test before touching a real workflow.

    Pro Tip: Certificates outlast secrets and don’t need quarterly rotation reminders. If your firm already runs a Key Vault or HashiCorp Vault for other service accounts, store the certificate there and reference it from n8n rather than pasting a secret into a credential field and forgetting about it.

    Rotate secrets on a fixed schedule regardless of which method you choose. A credential that quietly expires on a Friday afternoon billing-report automation is not a fun way to start Monday.

    What Graph Permissions Does Each n8n Node Need?

    Every node’s credential test and runtime calls depend on specific Microsoft Graph application permissions. Missing even one causes the workflow to fail silently or throw a generic authorization error. The credential test itself calls GET /v1.0/organization, which requires Organization.Read.All (or Directory.Read.All), according to the Service Principal credential docs.

    Node Typical operations Required Graph application permissions
    Credential test (all nodes) Verify tenant/app registration Organization.Read.All
    Microsoft Teams Send messages, manage channels ChannelMessage.Send, Channel.ReadBasic.All, Team.ReadBasic.All
    Microsoft Outlook Send mail, manage calendar Mail.Send, Mail.ReadWrite, Calendars.ReadWrite
    Microsoft Excel 365 Read/write worksheet rows Files.ReadWrite.All
    Microsoft OneDrive Upload, share files Files.ReadWrite.All

    Add permissions in the Entra app registration under “API permissions,” then click “Grant admin consent” for the tenant. That second click is what actually activates the permissions. The most common error readers hit is adding the permission but never granting consent, which leaves the app registered but functionally useless. Start with the narrowest permission set that satisfies your workflow, then expand only when a real operation fails.

    What Causes Most n8n Microsoft 365 Failures?

    Most failures trace back to one of four causes, and each has a fast fix.

    • Credential test fails immediately. Check for missing admin consent first, then confirm Organization.Read.All is granted. This is the single most common blocker.
    • “Resource not found” errors on Teams or Planner nodes. These nodes expect internal IDs, not display names. Pull the Team ID and Channel ID from the Graph Explorer or the URL bar in Teams before hardcoding them into your workflow.
    • Rate limit errors under load. Microsoft Graph throttles around 60 Teams messages per minute per app registration, so batch-heavy workflows need a Split in Batches node or a Wait node between sends.
    • Blocked operations under app-only credentials. Some Outlook or OneDrive calls expect a delegated user context. If an operation fails only under Service Principal but works under OAuth2, that is your signal.

    Pro Tip: If you’re migrating an existing OAuth2 workflow to Service Principal, run both credentials in parallel on a test tenant for a week before cutting over. Permission gaps only show up when the specific operation that needs them actually runs.

    Workflow Patterns Worth Piloting First

    Four patterns cover most of what mid-market professional-services firms actually need, and each is small enough to build in an afternoon.

    1. Invoice alert pipeline. An Outlook trigger watches a billing inbox, parses the attachment, writes a row to Excel or SharePoint, then posts a Teams alert to the finance channel. Add a Wait node between the Excel write and the Teams post to avoid racing the API.
    2. Lead-to-task automation. A CRM webhook normalizes incoming lead data, creates a Planner task with the client name and deadline, and pushes an assignment notice to the right Teams channel.
    3. Billing digest report. A scheduled trigger aggregates the week’s time entries from Excel, formats a summary, and sends a single batched Teams digest instead of one message per entry.
    4. Onboarding checklist trigger. A new-client Outlook email creates a To Do list and a OneDrive folder structure in one pass.

    Test every pattern on a sandbox tenant first, and keep a rollback note (which credential, which permissions, what changed) for anything touching a shared mailbox or channel.

    Security and Governance Considerations for Production Rollouts

    Your Graph API Base URL choice is the first governance decision, not an afterthought. Global tenants use the standard endpoint, but US Government, DOD, and China tenants each need their own base URL, and picking the wrong one silently breaks every call.

    Beyond that, a few controls matter most for compliance-minded firms:

    • Prefer certificate-based auth over client secrets where your security policy allows it, and store either in a proper secrets manager rather than an environment variable someone will forget about.
    • Assign the narrowest permission set each workflow actually needs, and review it quarterly as workflows change.
    • Log admin consent grants and review them alongside your existing access review cycle.
    • Pair your automation rollout with telemetry on Copilot license usage. Dormant licenses and unused automations tend to hide in the same blind spot.

    How Zera Turns n8n Automation Into Measured Copilot ROI

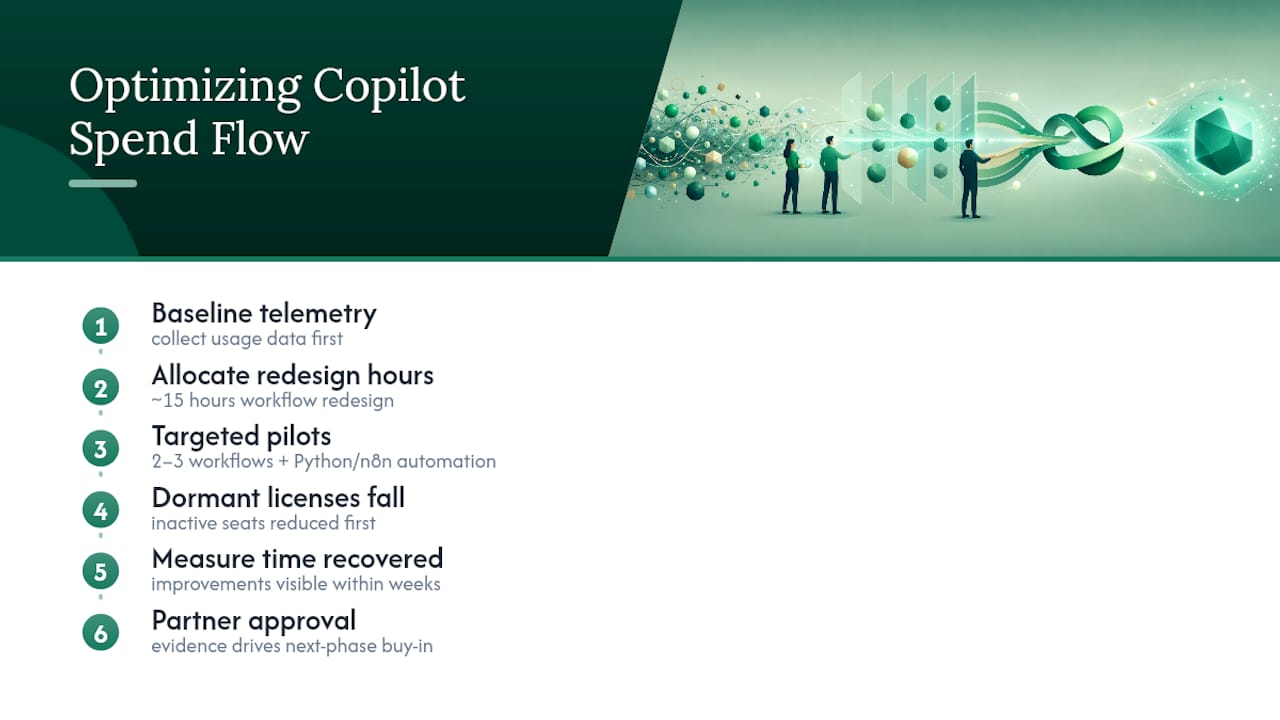
    n8n integration is a means, not the goal. Gozera treats it as one lever in a larger process: baseline Copilot usage with telemetry, flag dormant licenses draining budget, then rebuild the highest-friction workflows using n8n and Python where Copilot alone can’t close the gap.

    A typical engagement runs in stages:

    • Baseline measurement — telemetry on actual Copilot usage per seat, not assumed usage.
    • Workflow rebuild — identify the two or three processes (intake, billing, document routing) burning the most billable time.
    • Automation build — n8n handles the cross-platform logic; Copilot handles the drafting and summarization it’s actually good at.
    • ROI reporting — recovered billable hours, adoption lift, and license right-sizing, tracked against the baseline.

    Case studies and specific client metrics are available on request for firms evaluating a similar engagement.

    What IT Leaders Should Actually Do Next

    Pick one workflow that crosses at least two Microsoft 365 apps, something like invoice intake to Teams alert, and run it as a two-week sprint. Don’t start with a company-wide rollout. Start narrow, measure time saved against the manual process, and only then expand.
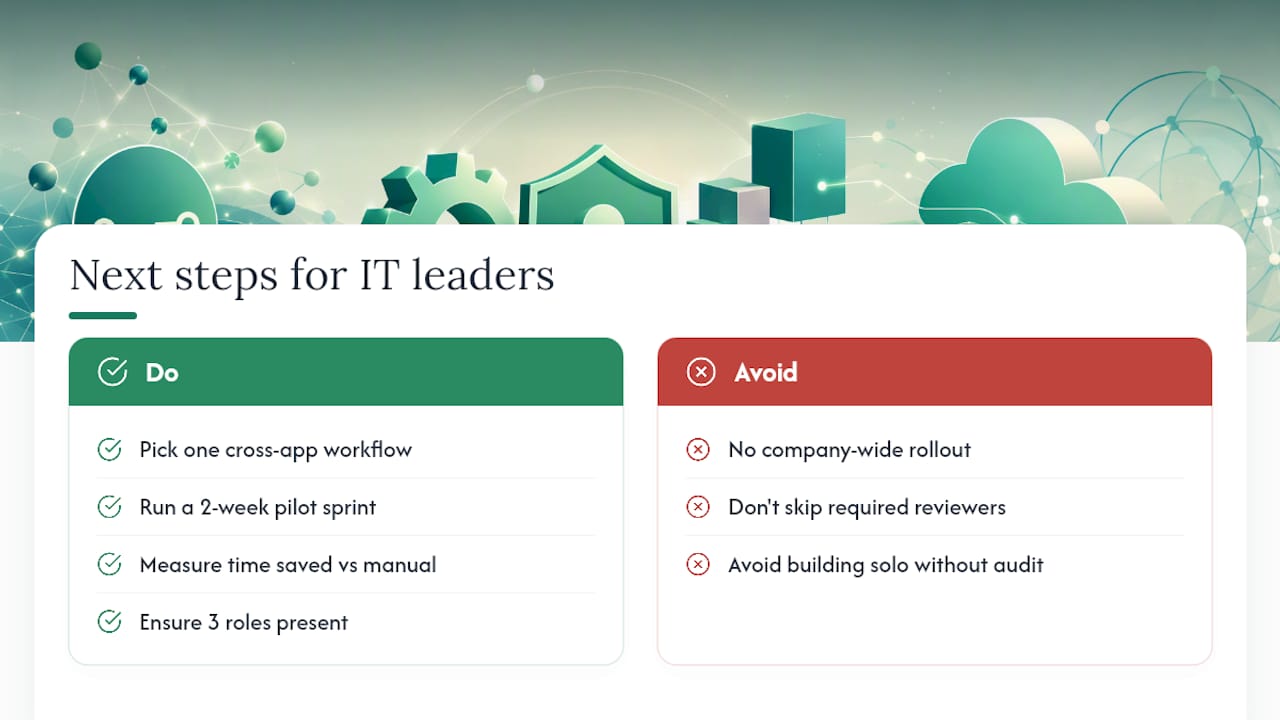
    What IT Leaders Should Actually Do Next — overview diagram

    You need three people in the room before you build anything: an identity admin who can grant consent without a two-week ticket queue, an automation owner who actually maintains the workflow after launch, and a security reviewer who signs off on permission scope. Skip any of the three and the pilot either stalls in Entra admin approvals or becomes shadow IT nobody can support.

    If you want a structured version of this instead of building it solo, consider running short assessment sprints that baseline your current Copilot usage and identify exactly which workflows are worth automating first. Visit Gozera’s Copilot adoption consulting to see how the audit works. For a broader playbook on where n8n fits against Copilot and Power Automate, see the n8n automation ROI guide.

    — Mad

    Where to Go Deeper on Setup Details

    The official docs cover the edge cases faster than any summary can. Start here:

    Sources

  • 2–4 Week Copilot for Knowledge Management, Mid Market Admins

    2–4 Week Copilot for Knowledge Management, Mid Market Admins

    Yes, Microsoft Copilot can serve as the semantic, context-aware layer for enterprise knowledge management, but only once you’ve prepared and governed your knowledge sources. The payoff is answers grounded in your actual organizational content instead of generic web results, pulled through Microsoft Graph. Your immediate move: run a scoped pilot with a short duration on one high-value use case and measure the telemetry before scaling further.


    TL;DR:

    • A successful Copilot deployment requires thorough knowledge source preparation, including clear titles, summaries, and regular content reviews, to ensure accuracy and relevance.
    • Limiting knowledge sources to around five with proper permissions generally yields better search results than grouping dozens, due to filtering and orchestration constraints.
    • Pilot programs should start narrow, with clear success criteria, and involve measuring active usage, citation rates, and time saved before expanding to other practice areas.
    • A governance framework must focus on content ownership, permission audits, source citation policies, and ongoing maintenance rather than overbuilding controls for unlikely risks.
    • Licensing costs depend on active user numbers and are often underestimated, so tracking seat utilization before and during deployment prevents overspending on unused licenses.

    Gozera
    Make Copilot Deliver Measurable Value
    Zera helps professional services firms measure usage, rebuild workflows, and turn Microsoft 365 Copilot into recoverable billable time.

    Explore Zera’s approach

    Table of Contents

    How Copilot Fits Into Enterprise Knowledge Management

    Copilot shows up in three distinct forms, and mixing them up wastes budget. Copilot Search is the universal search layer that uses Microsoft Graph plus behavioral signals to return semantic, context-aware answers rather than a stack of blue links. Copilot Chat is the conversational interface most employees already use daily. Copilot Studio agents are purpose-built bots your firm configures for a specific job, like answering partner questions about billing policy or client onboarding steps.

    The distinction matters for governance. Ground answers in your knowledge sources when accuracy and citation matter, such as compliance questions or client-specific procedures. Allow broader, ungrounded responses only for low-stakes brainstorming. Licensing works as an add-on to existing Microsoft 365 plans, so your rollout cost scales with seat count, not with the size of your knowledge base.

    What Should Be on Your Knowledge Hygiene Checklist?

    Microsoft’s own program managers are blunt about this: Copilot isn’t a magic bullet. Its answers are only as good as the content you feed it, and messy source libraries produce messy, occasionally wrong, answers.

    Run this checklist before ingesting anything at scale:

    1. Write clear, descriptive titles and summaries for every document.
    2. Break long documents into chunks with real subheadings, not walls of text.
    3. Strip personally identifiable information before ingestion.
    4. Add text descriptions to images. Copilot cannot read text embedded in a screenshot or scanned PDF.
    5. Fix or remove broken links across the source library.
    6. Convert email threads and chat exports into standalone content assets.

    Align your publication cycle with your ingestion cycle. Set expiration or deprecation dates on time-sensitive content, because asset age in Copilot is calculated from ingestion date, not from when a human last edited the file. Stale content that looks fresh is one of the fastest ways to lose trust in a pilot.

    Pro Tip: Preview a small sample of your source data inside Copilot Studio before running full ingestion. Catching a mislabeled folder on 50 documents costs you an afternoon; catching it after ingesting 50,000 costs you a re-index and a credibility hit with your pilot users.

    How Do You Control What Copilot Is Allowed to Surface?

    Copilot inherits the permission structure already sitting on your files. That’s a feature and a risk at the same time. If someone has broad SharePoint access they shouldn’t, Copilot will happily surface content through that same door.

    Governance essentials for admins:

    • Audit access controls on every source before connecting it, not after.
    • Decide deliberately whether to allow ungrounded responses for a given agent, or require it to cite a source for every answer.
    • Use bookmarks and authoritative answers to promote your best content over stale duplicates.
    • Keep ingestion logs and a removal workflow so you can prove what Copilot could see, and when, if a compliance question ever comes up.

    One structural limit worth planning around: once an agent has more than 25 knowledge sources attached, generative orchestration starts filtering which ones actually get searched. Wide isn’t always better. A tightly curated set of five sources with clean permissions will usually outperform a sprawling twenty-source agent nobody fully audited. For a deeper look at where Copilot’s guardrails hold and where they don’t, this breakdown of Copilot’s security guardrails is worth a read before you flip on broader access.

    How Do You Wire Copilot Into Real Workflows?

    Two integration patterns cover most professional-services use cases. Pattern A is agent-level knowledge paired with generative answers, suited to broad Q&A like “what’s our conflict-check process.” Pattern B is a topic-level flow action, like the Dynamics 365 knowledge article search, suited to precise, curated retrieval where you don’t want the model improvising.

    To build Pattern B: add the Power Automate template for knowledge article search, then attach it to a specific topic inside your Copilot Studio agent. This keeps retrieval scoped to a vetted article set instead of the model’s broader judgment.

    Practical limits to plan around:

    • Indexing time grows with source volume, so large connectors can take hours to reflect updates.
    • Source count limits push you toward Dataverse or Azure AI Search once a single collection gets unwieldy.
    • Agent Builder works for quick, disposable agents. Copilot Studio is the better home for anything you intend to govern and scale long term, per Microsoft’s own enterprise documentation.

    Firms building repeatable automation on top of these agents often find it useful to track how notes and decisions flow into actual deliverables. The Intent Ledger covers that workflow layer well if you’re mapping out what happens after the agent answers a question.

    How Do You Measure Whether the Pilot Is Working?

    Telemetry is the difference between “Copilot feels helpful” and knowing exactly which licenses are earning their cost. Five baseline metrics matter most:

    1. Active users, tracked weekly against total licenses assigned.
    2. Queries per user, which tells you whether adoption is real or a one-time trial.
    3. Asset citation rate, showing which documents Copilot actually leans on.
    4. Helpful response rate (HRR), gathered from user feedback on answers.
    5. Estimated time saved per query, even as a rough directional number.

    You’ll find most of this inside Copilot analytics and the Customer Service Copilot tab, supplemented with custom reports for asset age and citation frequency. Design the pilot itself around a fixed two to four week window, a single practice area, and clear roll-forward criteria decided before you start, not after the results come in.

    Pro Tip: Pull your license utilization report before the pilot even launches. Dormant seats you find on day one are money you’re already recovering, before a single workflow gets rebuilt.

    What Does a Real Implementation Playbook Look Like?

    A structured engagement usually runs through five phases: baseline measurement, a scoped pilot, workflow rebuild around what the data actually shows people need, targeted automation, and ongoing optimization. Consulting engagements typically build each phase around concrete artifacts rather than vague promises.

    Typical deliverables from a phased engagement:

    • A telemetry dashboard showing license usage and HRR trends over the pilot window
    • A written adoption playbook mapping which roles use which Copilot surface
    • A license optimization plan flagging dormant seats for reallocation or cancellation
    • A pilot report quantifying recovered billable hours for the practice area tested

    When evaluating any consulting partner for this work, ask for proof of baseline measurement methodology and a sample pilot report before signing anything. A firm that can’t show you what a report looks like probably hasn’t run one.

    What Governance Framework Actually Holds Up in Practice?

    Most firms overbuild governance for the wrong risk. The real exposure isn’t Copilot inventing facts. It’s Copilot surfacing something true that a client, a regulator, or opposing counsel should never have seen because a permission setting was wrong three years before anyone turned on AI search.

    Structure your policy around four layers instead of one giant document nobody reads. First, a content ownership layer: every knowledge source needs a named owner accountable for accuracy and staleness, not an abstract “IT owns this.” Second, an access layer: quarterly permission audits on your highest-risk SharePoint sites and Confluence spaces, because Copilot inherits whatever access already exists, for better or worse. Third, a response layer: define which agents require source citations by default and which can answer more freely, then document that decision so a new hire in eighteen months understands why.

    Fourth, and most overlooked, a lifecycle layer covering ingestion, review, and deprecation. Microsoft’s own guidance stresses that Copilot’s quality is bounded by source quality, and that treats knowledge hygiene as ongoing governance, not a one-time cleanup before launch. Assign a recurring calendar reminder, quarterly at minimum, to review what’s been ingested against what’s actually current.

    Four layers of knowledge governance

    Write this policy down in one page per layer. A governance framework that takes forty minutes to read gets followed. One that takes four hours gets filed and ignored, which defeats the entire point of having it.

    How Do You Actually Run a Copilot Pilot Start to Finish?

    Skip the enterprise rollout fantasy. Start narrow, prove value, then expand.

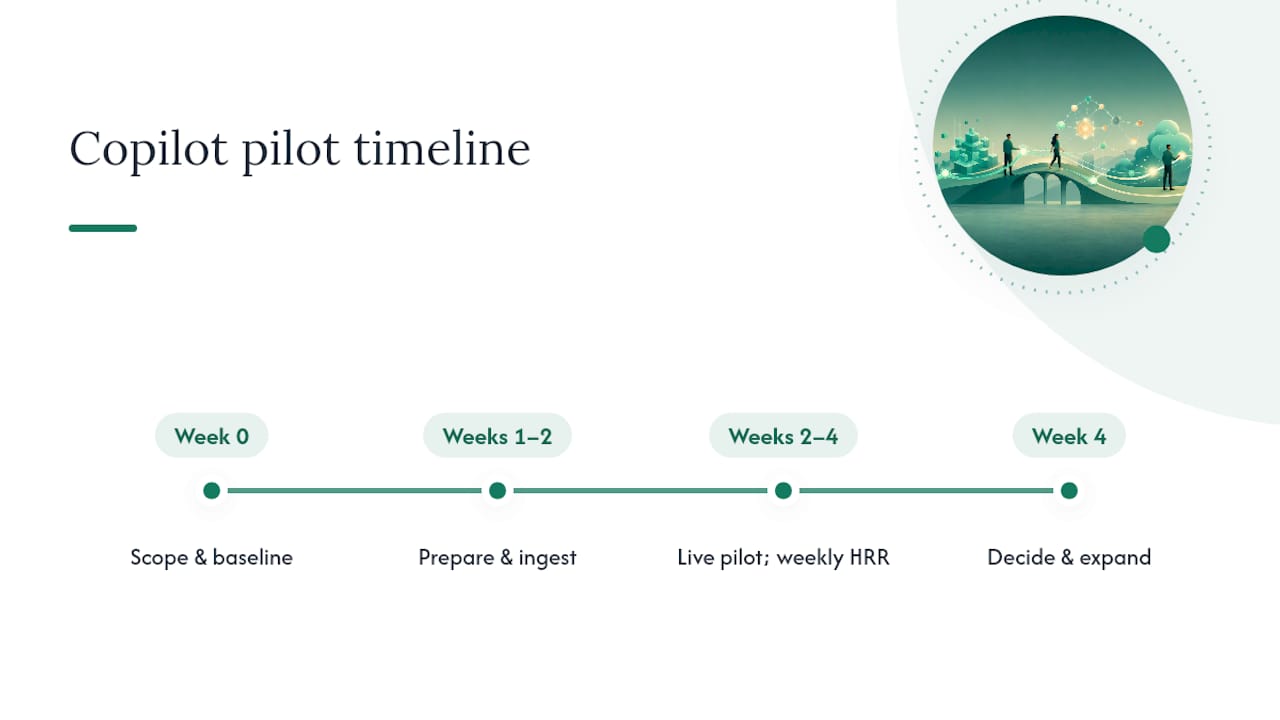
    Week zero: scope and baseline. Pick one practice area, ideally one with high query volume and clear pain, like new-associate onboarding questions or client intake procedures. Pull current license utilization and identify who’s actually going to use this daily. Set your success criteria now, not after you see promising results.

    Weeks one and two: prepare and ingest. Run the hygiene checklist against your chosen source library. Connect only the sources that library actually needs, resisting the urge to hook up every connector available. Preview sample data inside Copilot Studio and fix what’s obviously broken before full ingestion.

    Weeks two through four: live pilot. Give a small user group of limited size is sufficient, access to the configured agent or Copilot Search scope. Collect HRR feedback weekly, not just at the end. Watch citation rates to see which content is actually earning its keep.

    Week four: decide. Compare results against your pre-set success criteria. Calculate rough time saved per query and multiply by query volume to estimate recovered hours. If the numbers hold up, expand to a second practice area using the same playbook. If they don’t, diagnose whether it’s a content problem, a permissions problem, or genuinely low demand before scrapping the initiative. For a template on building this case for leadership, Gozera’s Copilot business case guide walks through the math firms use to get budget approved.

    Four-week Copilot pilot timeline

    What Goes Wrong Most Often With Copilot Deployments?

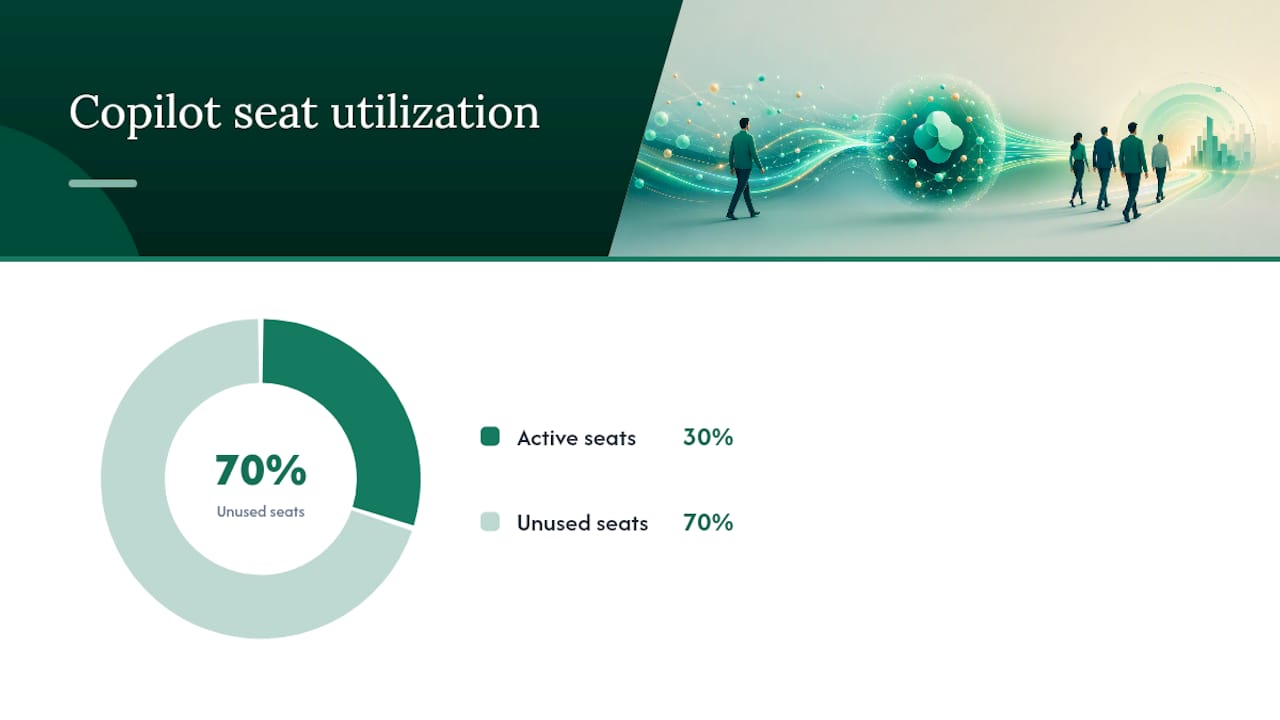
    The most common failure isn’t technical. It’s sequencing. Firms turn on Copilot licenses for everyone on day one, skip the hygiene work, and then wonder why adoption stalls at 20% three months later with most seats sitting idle.

    A second recurring pitfall is source sprawl. Teams connect every available system because it’s technically possible, then discover that once an agent crosses roughly 25 sources, generative orchestration starts filtering what actually gets searched, and results get less predictable, not more comprehensive. The fix is disciplined scoping from the start, not damage control later.

    A third pitfall is treating ingestion as a one-time project. Content goes stale, asset age calculates from ingestion date rather than last edit, and nobody notices until an agent confidently cites a policy that changed eight months ago. Build a recurring re-ingestion cadence into whoever owns each source, not into a calendar reminder that gets snoozed.

    A fourth pitfall, particularly common in law and accounting firms handling sensitive client data, is skipping the permission audit before connecting a source. Copilot respects existing access controls, which means any pre-existing permission mistake gets amplified the moment search becomes smarter and more visible. Audit first, connect second, always in that order.

    Finally, firms underestimate the citation gap. If your agent isn’t set to require source citations, users can’t verify an answer, and skepticism kills adoption faster than any bug. Requiring citations by default costs you a small amount of response speed and buys you the trust that actually drives usage numbers up.

    How Should You Train Staff on Copilot Without a Six-Month Rollout?

    Traditional enterprise change management assumes months of training decks and mandatory workshops. Professional-services firms don’t have that runway, and frankly don’t need it if the rollout is scoped correctly.

    Train around real tasks, not features. Instead of a generic “here’s what Copilot can do” session, show associates exactly how to ask it to summarize a deposition transcript or draft a first-pass client memo from existing templates. Task-specific training sticks; feature tours don’t.

    Identify two or three power users per practice group early and let them become informal champions. People trust a colleague who says “I used this to cut an hour off my Friday billing review” far more than they trust an IT memo. This costs nothing and moves faster than formal enablement sessions.

    Set expectations about accuracy explicitly. Tell staff directly that Copilot answers require verification against source documents, especially for anything client-facing or billable. This isn’t a disclaimer; it’s the difference between an associate who becomes a power user and one who gets burned once and quits using the tool entirely.

    Measure training success the same way you measure the pilot: through actual usage telemetry, not attendance at a training session. If query volume and HRR climb after a lunch-and-learn, the training worked. If they don’t, the tool isn’t the problem, the rollout sequencing is. Gozera’s implementation guide for IT leaders covers a rollout sequence built around this exact logic.

    What Should You Budget for Licensing as Usage Scales?

    Copilot licensing works as a per-seat add-on layered on top of your existing Microsoft 365 subscription, which means your cost scales linearly with headcount rather than with how much knowledge you’ve ingested or how many agents you’ve built. That’s good news for budgeting and bad news for firms that assign licenses broadly and then discover half of them sit unused.

    The real cost risk isn’t the license price. It’s paying for seats nobody activates. A 500-person firm that licenses Copilot for 300 employees but sees active weekly usage from a minority of them isn’t running an AI strategy, it’s subsidizing a rounding error. This is precisely the gap telemetry is built to catch, and precisely why a pilot that measures active users before a full rollout matters more than the sticker price of any tier.

    Budget for three cost centers, not one: the licenses themselves, the ingestion and hygiene work to prepare knowledge sources properly, and ongoing optimization to keep content fresh and agents tuned. Firms that budget only for the license line item consistently underestimate total cost of ownership, then wonder why adoption and ROI don’t match the invoice. Gozera’s ROI breakdown for mid-market firms walks through how these three cost centers typically split out in practice, and where firms tend to overspend without realizing it.

    Publisher Perspective: Prioritization for Mid-Market Firms

    Small, tightly scoped pilots beat wide indexing almost every time in professional services, where a permission mistake on client files carries real liability. Speed to value matters, but not at the cost of an access audit you skipped to hit a launch date. If you remember one thing from this guide, make it this: measure before you rebuild, and never license more seats than your telemetry says you’re actually using.

    — Mad

    Get a Copilot ROI Audit for Your Firm

    Some consulting firms focus on the gap between what firms pay for Copilot licenses and what those licenses actually produce in recovered billable time. Instead of another rollout deck, an engagement starts with real telemetry, showing exactly which seats are active, which are dormant, and where a rebuilt workflow would pay for itself fastest.

    Gozera

    A typical first engagement delivers a usage baseline, a scoped pilot on one practice area, and a written adoption plan your partners can actually act on, not a slide deck that gets filed away. Some teams pair enterprise governance experience with hands-on automation work using Python and n8n, closing the gaps a license alone never will. If your firm is sitting on Copilot seats you’re not sure are earning their cost, start a Copilot ROI audit with Gozera and get a baseline before you spend another quarter guessing.

    Sources

    Copilot’s connector ecosystem is wide, but not every source behaves the same way once it’s ingested. Microsoft 365 Copilot supports more than 100 prebuilt connectors for pulling third-party platform data into Microsoft Graph, where Copilot experiences can find it.

    Featured sources most firms start with:

    Advanced sources for firms with more mature stacks:

    Unstructured sources like Confluence get ingested at the collection level, meaning you can’t cherry-pick individual pages. Reorganize content into logical collections first. Start with a small, curated set for any critical agent rather than indexing everything at once. Available connectors also vary by tenant configuration and license tier, so confirm what’s actually enabled before you plan around a source that isn’t there yet.

  • Recover Billable Time With Copilot Prompt Library for Midmarket Firms

    Recover Billable Time With Copilot Prompt Library for Midmarket Firms

    A Copilot prompt library is a saved collection of reusable prompts and templates, primarily Microsoft’s own Prompt Gallery and Copilot Studio template set, built to speed up repeatable work in Word, Excel, Outlook, and Teams. The immediate value is standardization: instead of every partner or associate typing a different version of the same request, your firm saves, shares, and refines role-specific prompts once. Start in the Prompt Gallery inside Copilot Chat, then extend into Copilot Studio for anything workflow-heavy.


    TL;DR:

    • Most firms overlook the importance of measuring prompt reuse and productivity gains rather than just building a large library of prompts.
    • Proper governance requires clear permission tiers, regular audits, and sensitivity labeling to prevent data leaks and outdated prompts from remaining active.
    • Customizing prompts with firm-specific terminology, formatting instructions, and task-focused variables significantly improves output quality for professional services.
    • Community prompt repositories like GitHub can serve as valuable sources but require thorough testing, security review, and adaptation before deployment.
    • Adopting prompts as part of a broader workflow infrastructure with ongoing telemetry tracking offers better ROI than simply browsing or sharing templates.

    Table of Contents

    What the Copilot Prompt Library Actually Is

    Microsoft runs two distinct systems under this umbrella, and mixing them up wastes time. The Prompt Gallery is what most Microsoft 365 users see inside Copilot and Copilot Chat: a mix of Microsoft-authored suggested prompts and prompts your organization or teammates have saved. The Copilot Studio prompt library is a separate, more technical set of templates meant for building agents and integrating with Power Apps or Power Automate.

    Both matter for firms, but they solve different problems. The Prompt Gallery handles daily individual and team work. Copilot Studio handles process automation.

    Where prompts live matters more than most IT leaders realize. Prompt Gallery entries, including anything your team saves or shares, stay within the tenant boundary in the Microsoft 365 Substrate data store. That’s not marketing language. It’s the technical reason a law firm’s internal deposition-summary prompt doesn’t leak into a public model’s training data.

    When evaluating a prompt, whether it’s Microsoft’s or a colleague’s, check three things:

    • Source: is it Microsoft-authored, org-published, or a personal save from a teammate?
    • Recommended apps: does it specify Word, Excel, or Teams, or is it app-agnostic?
    • Edit history: has anyone refined it since it was first saved, or is it the untouched default?

    How To Find The Prompt Library In Copilot And Copilot Studio

    Microsoft splits access between public reference pages and the authenticated experience inside your Microsoft 365 apps. You don’t need a license to browse the general how-to documentation, but you do need to be signed in to actually save, edit, or share a prompt.

    1. Open Copilot Chat and look at the compose box. Type your request directly, or type “/” to reference specific files, people, or meetings so Copilot grounds its answer in your actual business data instead of generic web knowledge.
    2. Click the Prompt Gallery icon inside Copilot Chat. This surfaces Microsoft’s suggested prompts alongside anything saved by you or your team.
    3. Check Teams and Outlook for the same gallery. Microsoft rolled prompt discovery into Teams and Outlook directly, so a prompt saved in one app often surfaces in another.
    4. Go to Copilot Studio for template-based building. This is a separate portal from everyday Copilot Chat and is where you’ll build agents, not just run one-off prompts.

    If your firm hasn’t rolled out licenses evenly, this is also where dormant seats become visible. Someone with a Copilot license who has never opened the Prompt Gallery is a signal worth tracking, not ignoring.

    Using, Saving, And Sharing Prompts Across Your Team

    The workflow that actually sticks looks like this: try a prompt, tweak it for your firm’s language, save it, then share it so nobody else has to reinvent it.

    Start by running a suggested prompt as-is, then explore how tools like Minuted — meeting notes that write themselves up can automate note-taking from client-facing meetings. Then customize it, swap “summarize this contract” for “summarize this contract and flag any indemnification clauses,” and save the result to Your prompts for personal reuse or to a Teams collection so your practice group inherits it. Microsoft’s gallery update added sharing via copy link, a Teams tab, or email, plus a “like” mechanism and leaderboards that surface which prompts a team actually uses.

    Governance shouldn’t be an afterthought here. Decide early who can publish an org-level prompt versus a personal one, and set a quarterly review so stale prompts (ones referencing a retired template or an old client naming convention) get retired.

    A few starter templates worth adapting:

    • Word: “Draft a client engagement letter for [matter type], using our standard indemnification language and a 30-day payment term.”
    • Excel: “Summarize this billing spreadsheet by partner and flag any invoice over 90 days outstanding.”
    • PowerPoint: “Turn these five bullet points into a three-slide client update deck in our firm’s tone: direct, no jargon.”
    • Outlook: “Draft a follow-up email to [client] summarizing today’s call and listing next steps with owners and dates.”

    Pro Tip: Save the prompt, not just the output. A well-worded prompt saved to your team’s collection compounds in value every time someone reuses it, while a one-off Copilot answer disappears the moment the chat closes.

    For firms managing broader workflow rollouts, Gozera’s guide on Microsoft 365 workflow tools covers how prompt sharing fits into a larger adoption plan.

    Copilot Studio Templates: From Prompt To Agent

    Copilot Studio’s prompt library operates differently. Its templates are built for reuse inside automated systems, not just individual chat sessions, and Microsoft Learn documents how to copy, edit, and embed them into Power Apps or Power Automate flows.

    A Copilot Studio template has four working parts:

    • Instruction text: the core task definition, similar to a Prompt Gallery entry but written for repeatable automation.
    • Input slots: placeholders where a Power Automate flow inserts variable data, like a client name or matter number.
    • Model and temperature settings: controls that determine how creative or literal the output should be, adjustable per template.
    • Output selection: whether the result feeds a Dataverse table, an email, or a downstream app.

    Copy a template, edit the instruction text for your firm’s terminology, adjust temperature down for anything client-facing (lower temperature means more predictable, less improvised phrasing), and test before deploying.

    The decision point is scale. A single prompt handles a one-off task. Build an actual agent when the work involves multiple steps, decision branches, or needs to run without a human triggering it every time, like routing incoming intake forms to the right practice group automatically.

    Community Prompt Libraries Worth Borrowing From

    Microsoft’s own galleries aren’t the only production-ready source. The pnp/copilot-prompts repository on GitHub contains 112 prompt samples and 31 agent instruction templates, organized into samples, agent instructions, and skills folders, structured closely enough to Microsoft’s own conventions that adapting them is straightforward. Other community collections, like maliklogix/PromptsForAITools, offer broader system-prompt patterns across different AI tools.

    Before anything from GitHub touches production, run it through a short checklist:

    • Security review: confirm the prompt doesn’t request sensitive data handling in ways that conflict with your tenant’s data policies.
    • Tenantization: rewrite any placeholder company names, document formats, or terminology to match your firm.
    • Testing: run it against real (but non-confidential) sample documents before trusting the output on client work.
    • Add to your collection: once vetted, save it to your team’s Prompt Gallery collection so it inherits the same tenant-boundary protections as everything else.

    Treat these repositories as inspiration and starting structure, not drop-in production code. The gap between “close enough” and “safe for client work” is exactly where the review step earns its time.

    Building A Living Prompt Library That Actually Pays Off

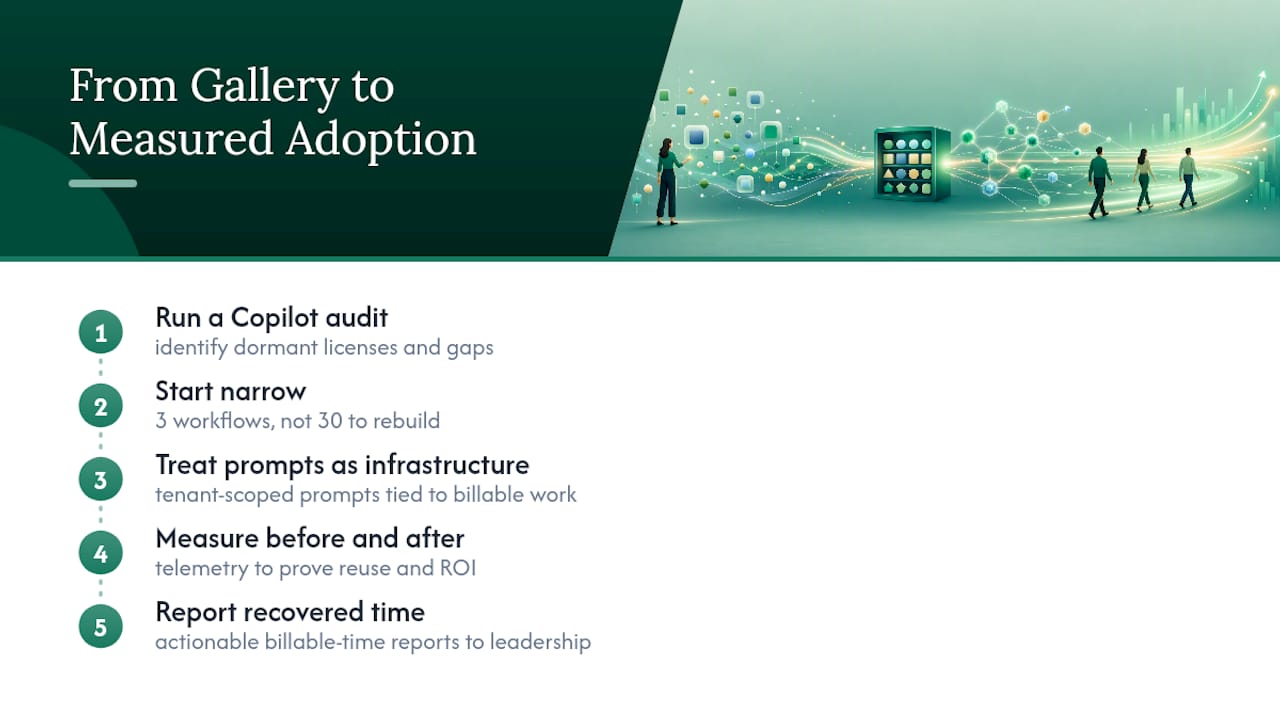
    Most firms treat the Prompt Gallery as a novelty feature. The ones seeing real return treat it as infrastructure, and that shift starts with picking a narrow, measurable pilot instead of rolling Copilot out firm-wide and hoping adoption follows.

    1. Pick three billable workflows first. A contract review process, a client status update, and a billing reconciliation task are enough to prove value without overwhelming your rollout team.
    2. Build role-specific prompts for each. A litigation associate and a corporate associate need different phrasing even for a similar task like summarizing a document.
    3. Measure baseline productivity before you deploy anything. You can’t prove time saved if you never captured how long the task took beforehand.
    4. Track usage telemetry after rollout. Identify which licenses sit idle and which prompts actually get reused, then report recovered billable hours back to leadership in concrete terms.
    5. Layer in governance as usage grows. Tenant-scoped prompts, sensitivity labels on anything touching client data, and a scheduled quarterly review keep the library from becoming a graveyard of outdated templates.

    Pro Tip: Iterating on a prompt beats hunting for the “perfect” one. Microsoft’s own guidance on the Prompt Gallery treats refinement as the expected workflow, not a failure state, so build that expectation into your firm’s training from day one.

    This is a common pattern among firms working with mid-market clients: curated templates, short enablement sessions, then telemetry-driven iteration rather than a one-time training day nobody remembers a month later. Firms considering a structured rollout can review the Copilot implementation guide for IT leaders for the fuller playbook, or the law firm ROI playbook for sector-specific examples.

    Keeping Your Prompt Library Current Instead Of Stale

    A prompt library without version control turns into digital clutter within a few months. Someone edits a shared prompt, the change breaks a downstream workflow, and nobody can tell which version is currently live.

    Treat prompt updates the way you’d treat any shared document: track who changed what and when. The Prompt Gallery itself shows edit and save history at a basic level, but firms serious about consistency should keep a lightweight external log too, even a simple spreadsheet noting the prompt name, the date of the last edit, who made it, and why.

    Set a recurring review cadence rather than reacting only when something breaks. Quarterly works well for most firms: check which prompts are still being used (the leaderboard data helps here), which reference outdated terminology or retired document templates, and which need retiring outright. A prompt built around last year’s engagement letter format is worse than no prompt at all, because it produces confidently wrong output.

    When you do update a widely shared prompt, communicate the change. A one-line note in your Teams channel, “updated the client intake summary prompt to include new conflict-check language”, prevents someone from assuming their saved version is still current when it’s actually been superseded. Version drift is invisible until a partner catches an error in a client deliverable, and by then the cost is much higher than a five-minute review would have been.

    Who Should Be Allowed To Touch The Library

    Permissions get overlooked because the Prompt Gallery feels like a low-stakes feature. Treat it with the same rigor as document permissions, because a prompt that pulls client data through a poorly scoped instruction is a real exposure.

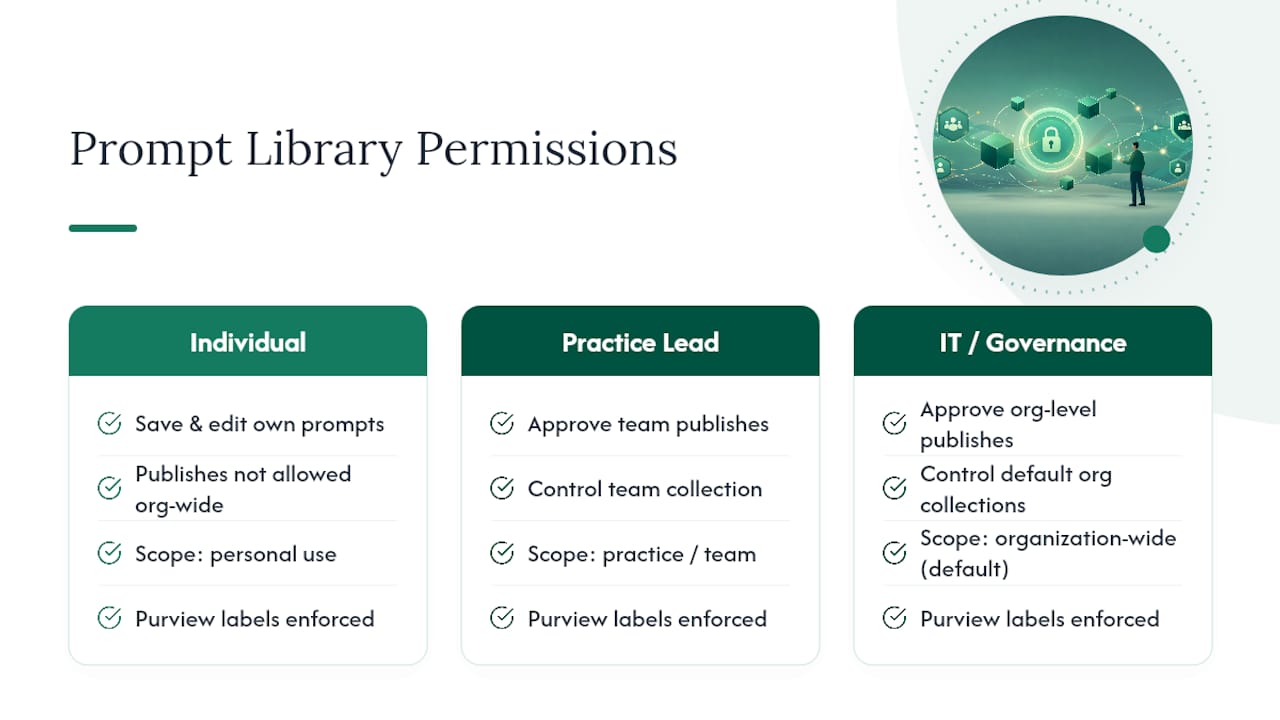
    Set three permission tiers rather than an all-or-nothing model. Individual users should freely save and edit their own prompts. A smaller group, practice group leads or a designated Copilot champion, should control what gets published to a team collection. Only IT or a governance committee should approve anything published at the organization level, since that’s what every employee will see by default.

    Three-tier prompt library permissions model

    Sensitivity labels matter here too. If a prompt is designed to summarize documents that might contain privileged or confidential client information, make sure the underlying data sources respect your existing Microsoft Purview labels. A prompt doesn’t override your firm’s existing information barriers, but a poorly built one can accidentally surface data across those barriers if permissions aren’t checked first.

    Audit who has publishing rights every six months, not only when someone leaves the firm. Turnover in mid-market firms is common enough that former employees retaining publish access to shared collections is a real, avoidable gap.

    Customizing Prompts For Your Firm’s Actual Work

    Generic prompts fail in professional-services settings because the generic version doesn’t know your firm’s terminology, formatting standards, or client expectations. A prompt that says “summarize this document” produces a different, less useful result than one that says “summarize this document in the format our litigation team uses for case status memos.”

    Start customization by identifying the specific output your firm actually wants, not the output a default Microsoft prompt happens to produce. If your accounting practice needs variance explanations formatted a certain way for partner review, build that formatting instruction directly into the saved prompt rather than fixing it after every single output.

    Troubleshooting a prompt that isn’t working usually comes down to one of three issues: the instruction is too vague, the model temperature is mismatched to the task (creative writing needs a higher setting, compliance summaries need a lower one), or the prompt is missing a reference to the actual file or data source it needs. Test each variable separately instead of rewriting the whole prompt at once. Change the temperature first if outputs feel too repetitive or too erratic, then adjust instruction wording if the content itself misses the mark.

    Document drafting is a common failure point worth calling out specifically. Firms using Copilot for document drafting often find that a prompt working well for a simple memo breaks down entirely for a 40-page contract, because the instruction doesn’t account for section-by-section consistency. Build separate prompts for short-form and long-form drafting rather than forcing one template to handle both.

    Here’s what the official guidance gets right and where it stops short. Microsoft’s Prompt Gallery and Copilot Studio templates are genuinely well built, tenant-scoped, versioned, and increasingly easy to share across a team. The documentation is thorough. The GitHub communities extending it, particularly pnp/copilot-prompts, are more production-ready than most internal IT teams expect from open-source resources.

    But browsing a gallery isn’t the same as adoption, and adoption isn’t the same as ROI. The uncomfortable pattern across mid-market professional-services firms is a stack of unused Copilot licenses sitting next to a handful of people who found three or four prompts they love and never looked further. Neither official galleries nor community repositories fix that gap on their own. They’re inputs, not outcomes.

    The Gap Between Gallery Browsing And Real Adoption — overview diagram

    What actually moves the needle is treating the prompt library as living infrastructure tied to specific billable workflows, measured before and after, not as a feature to demo once in a training session. A firm that saves twelve prompts but never tracks whether anyone reuses them has built a gallery, not a productivity gain. The firms getting real return start narrower than they expect, three workflows, not thirty, and let telemetry tell them where to expand next.

    If there’s one thing worth prioritizing above everything else in this article: measure before you customize. A perfectly worded prompt for a workflow nobody tracks is invisible value.

    — Mad

    Firms ready to move past gallery browsing and into measured adoption can start with a Copilot ROI and adoption audit that aims to identify dormant licenses, rebuild high-value workflows around tenant-scoped prompts, and report recovered billable time back to leadership in actionable terms.

    Sources

  • Admins: Recover Billable Time in 4–6 Weeks with Copilot for Time Entry

    Admins: Recover Billable Time in 4–6 Weeks with Copilot for Time Entry

    Copilot for time entry drafts your current-week time entries and short external comments so professionals spend less time completing timesheets. Admins have to enable the feature, and someone still has to review every draft before it posts. The payoff shows up in fewer half-finished timesheets and faster billing cycles, not in a hands-off system that logs hours for you.


    TL;DR:

    • Copilot in time entry only suggests current-week hours based on active project assignments, so outdated data may lead to inaccurate drafts.
    • The feature requires both the Project Operations version to be compatible and tenant-wide activation of Copilot in model-driven apps.
    • It is essential to manually refresh the grid after AI actions, as the interface does not auto-update with new drafts or suggestions.
    • Distributed teams should be aware that Copilot uses UTC for week boundaries, which could cause suggestions to appear in the wrong week for late or night-shift workers.
    • Firms should pilot Copilot with one team for at least four weeks, measure recovered billable hours, and avoid firm-wide rollout before understanding actual adoption and ROI.

    Table of Contents

    Availability and Prerequisites for Copilot in Time Entry

    Before anyone on your team sees a Copilot sidecar, check three things. First, confirm your Project Operations version, since Copilot in time entry is only available from specific general-availability releases onward. Second, verify that Copilot is turned on tenant-wide for model-driven apps. Third, understand a quirk that trips up distributed teams: Copilot only suggests entries for the current week and uses UTC to determine which week that is, not the user’s local time zone.

    That UTC behavior matters more than it sounds. A consultant in Vancouver working late Sunday night might find Copilot has already rolled into a new week by its own clock.

    • Check your Project Operations version number in admin settings before enabling anything.
    • Confirm Microsoft 365 Copilot license covers model-driven apps for your tenant.
    • Warn distributed or late-shift teams about the UTC week boundary in advance to avoid confusion.

    How Do You Enable or Disable Copilot in Time Entry?

    Enabling the feature is a five-minute job for an admin with the right access. Disabling it is just as fast if you decide the timing isn’t right for your team yet.

    1. Go to Settings → Parameters → Project Parameters.
    2. Open the Feature Control tab.
    3. Toggle Enable Copilot in time entry to On.
    4. Save and publish the parameter change.
    5. Log in as a test user and open Time Entries to confirm the Copilot icon appears next to the entry grid.
    6. If the icon is missing, check the tenant-level Copilot setting before assuming the feature flag failed.

    The most common mix-up here is confusing the Project Operations feature flag with tenant Copilot enablement. Both have to be on. One without the other leaves users staring at a normal grid with no sidecar in sight.

    How Do You Access the Copilot Sidecar in Time Entry?

    Time-entry workspace beside Copilot sidecar

    Users open the sidecar by clicking the Copilot icon next to their avatar in the top corner of the time entry screen. From there, a chat pane opens where plain-language commands do the work that used to take several clicks.

    A handful of starter commands cover most needs:

    • “Log my time” to trigger a draft based on current project assignments.
    • “Create time entries” for a more direct version of the same action.
    • “Generate comments” to produce short external narratives for existing entries.
    • A week-selection prompt, since Copilot will ask which week you mean if it’s ambiguous.

    Watch for the small sparkle icon on any row Copilot touches. That’s the visual cue marking AI-generated content, and it disappears the moment a user edits the entry manually. One easy-to-miss detail: the grid does not refresh automatically after an AI action, so you have to hit refresh yourself to see new drafts appear.

    How to Log Time With Copilot Without Creating Gaps or Duplicates

    Getting a clean week of time entries with Copilot follows a fairly consistent pattern once you’ve done it a few times.

    1. Open Time Entries for the current week.
    2. Click the Copilot icon to launch the sidecar.
    3. Type “Log my time” or “Create time entries.”
    4. Confirm the week Copilot proposes, correcting it if the UTC boundary caught it wrong.
    5. Review the draft entries against your actual project assignments.
    6. Manually refresh the grid to see the new rows.
    7. Edit any entry that’s missing hours, wrong task codes, or the wrong role.
    8. Save.

    Copilot pulls from active project assignments to build its suggestions, and it’s built to skip entries that already exist so you don’t end up with duplicate rows for the same task. The catch is that stale assignment data produces stale suggestions. If someone rolled off a project last week and the assignment record hasn’t caught up, Copilot may draft time against work that’s already finished.

    Pro Tip: Run a five-minute assignment audit every Monday morning before your team touches Copilot. Clean inputs are the single biggest driver of accurate drafts, and it costs less time than fixing bad entries on Friday.

    Generating External Comments With Copilot

    Time entry narratives are usually the part professionals procrastinate on, and they’re also the part clients actually read on an invoice. Copilot shortens that gap.

    • Trigger the “Generate comments” command inside the sidecar and choose the week you want narratives for.
    • Copilot drafts short, editable comments pulling from the Project, Project Task, Role, and Duration fields tied to each entry, typically staying under 100 characters per draft.
    • Review each generated comment inline before anything gets saved. Edited text loses the sparkle icon, which is useful for approvers scanning for AI-assisted content.
    • Click Save all once you’re satisfied with the batch.

    Comment generation runs on Azure OpenAI’s language model capabilities, and Microsoft’s own guidance is explicit that these drafts need human review before they hit a client invoice. Treat the 100-character guideline as a floor for editing, not a finished product.

    Time Entry Agent (Preview): Admin Publish Checklist

    If your firm wants time capture inside Microsoft Teams rather than the Dynamics 365 grid, the Time Entry Agent preview is the tool built for that. It syncs project assignments and calendar events into draft entries and can send reminder-style alerts, but it requires Project Operations version 4.140.0.239 or later.

    Getting it live takes more coordination than the standard feature toggle, requiring detailed implementation blueprints for automation workflows like those in AI SDR vs. SDR Agency — An Honest Comparison.

    1. Create a dedicated agent user with the correct security roles.
    2. Activate every required Power Automate flow tied to the agent.
    3. Enable the Time Entry Agent feature flag in your environment.
    4. Publish the agent from Copilot Studio.
    5. If you want Teams distribution, a global admin publishes the app and sets any required app setup policies.
    • Flows must show as ON in the correct sequence, or publishing from Copilot Studio will simply fail with no clear error pointing to the cause.
    • Skipping the dedicated agent user is one of the most common reasons the agent behaves inconsistently after publishing.

    Responsible AI: Limits and Governance Controls That Matter

    Copilot is a drafting tool, not an autonomous timekeeper. Microsoft’s own responsible AI guidance frames it as a review-and-confirm workflow, and firms that treat it that way avoid most of the friction that comes with rolling out AI to billable professionals.

    • Scope is current-week only. There’s no retroactive logging, so missed weeks still require manual entry.
    • Week selection follows UTC, not local time, which can misfire near midnight for distributed teams.
    • The grid never refreshes on its own after an AI action; someone has to click refresh.
    • Generated comment fields aren’t customizable beyond standard editing.

    Pro Tip: Set a simple rule: any entry or comment carrying the sparkle icon gets a second look from a project lead before it’s billed. That one habit does more for accuracy than any feature setting.

    Give approvers visibility into which entries were AI-generated versus manually typed, and check usage telemetry periodically to confirm the feature is actually being used rather than sitting idle.

    Fixing the Most Common Copilot Time Entry Problems

    Most issues fall into three buckets, and each has a fast diagnostic path.

    • Copilot icon missing: Check tenant-wide Copilot enablement for model-driven apps first, then confirm the Project Parameters feature flag is on. Both need to be active.
    • Time Entry Agent won’t publish: Confirm every required Power Automate flow shows ON, in sequence, and that the agent user has the correct roles assigned. A single flow left off will block publishing.
    • Suggested entries missing or duplicated: Check that project assignments are current. Outdated assignment records are the top cause of missing suggestions, and a stale entry left in the grid is the top cause of duplicates.
    • Customizations not working as expected: Out-of-the-box Copilot workflows don’t automatically pick up existing Time Entry customizations, so a short integration sprint, or a Microsoft support ticket for complex cases, is often necessary.

    Turning Copilot Adoption Into Recoverable Billable Time

    Enabling Copilot in time entry is a configuration task. Getting a real return from it is an adoption problem, and that’s where most mid-market firms lose the thread. Start with telemetry, not enthusiasm: measure how many Copilot licenses are actually being used before you roll anything out further, and set a baseline for time-to-invoice across your busiest practice group.

    Run a focused pilot next. Pick one high-frequency team, turn on time entry drafting plus comment generation, and track recovered billable time over four to six weeks. Firms that log time contemporaneously with AI-assisted narratives tend to see fewer fee disputes and faster billing cycles as a direct result.

    • Baseline dormant license usage before expanding rollout to more teams.
    • Pilot with one team for four to six weeks and measure recovered hours directly.
    • Use Power Automate or lightweight scripting to close repetitive gaps Copilot doesn’t cover natively.
    • Report ROI in concrete terms: recovered hours, fewer billing disputes, shorter time-to-invoice.

    Law firms in particular tend to see fast wins here, since narrative time entries carry outsized weight on client invoices. A Copilot ROI playbook for law firms walks through how one practice group structured its pilot around exactly this metric.

    Essential Resources for Enabling Copilot in Time Entry

    Where Firms Actually Recover Billable Time With Copilot

    The gap between what Copilot promises and what firms actually capture almost always comes down to sequencing. Pilot with one team first, instrument telemetry from day one, and resist the urge to roll it out firm-wide before you’ve seen four weeks of real usage data. Prioritize a review-by-user workflow over speed. Every dispute avoided and every hour recovered is the metric that proves the license was worth paying for.

    — Mad

    Sources

  • 4 Copilot Acceptable Use Policy Rules to Harden Mid Market IT Tenants

    4 Copilot Acceptable Use Policy Rules to Harden Mid Market IT Tenants

    A working Copilot acceptable use policy requires four things: mandatory human verification of outputs used in client or regulated work, a hard ban on entering privileged or regulated personal data into prompts, tenant guardrails (DLP rules, sensitivity labels, knowledge exclusions) that enforce those rules technically, and logged training records tied to license access. If your firm hasn’t done this yet, the fastest fix is a tenant configuration and data classification audit this quarter, before another attorney or accountant pastes a client file into a chat window.


    TL;DR:

    • Staff should strictly map data classification tiers to Copilot permissions to prevent unapproved confidential or privileged information from being processed.
    • Technical controls like sensitivity labels, DLP rules, and conditional access are essential to enforce the policy and should be reviewed quarterly for effectiveness.
    • Human oversight must include mandatory training, clear prohibited uses, and signed attestations before license activation to ensure responsible AI use.
    • Disclosing Copilot involvement in outputs and retaining logs for security reviews are key steps to maintain transparency and compliance.
    • Incident response requires swift action to isolate, preserve logs, notify security, and review the breach, with policies regularly updated based on lessons learned.

    Table of Contents

    What Should a Copilot Acceptable Use Policy Cover?

    A usable AUP is not a one-page disclaimer. It’s a governance document that assigns responsibility, restricts inputs, and creates a paper trail. The University of Ottawa’s Copilot guidance treats the policy as a full framework mapping data classification to allowed workflows, not a bolt-on notice, and that structure holds up well for professional services firms to adapt it to their own risk profile.

    Nine elements belong in every version:

    • Scope and audience. Name which employees, contractors, and Microsoft 365 services (Copilot Chat, Word, Teams, Outlook) the policy governs.
    • Permitted uses. Drafting first-pass memos, summarizing internal meeting notes, generating boilerplate correspondence.
    • Prohibited uses. A specific list, not a vague “use responsibly” line.
    • Data input rules. Which classification tiers may touch Copilot and which never do.
    • Human-in-the-loop requirements. Who checks outputs before they reach a client or a court filing.
    • Training and attestation. Mandatory before license activation.
    • Technical controls. DLP, sensitivity labels, conditional access.
    • Retention and disclosure rules. How long chat logs live and when Copilot use gets disclosed.
    • Enforcement actions. What happens after a violation.

    Number your clauses so staff can cite section 4.2 instead of paraphrasing intent. That single habit cuts down on the “I thought that meant something else” excuse during an incident review.

    What Uses Should a Copilot Policy Explicitly Ban?

    Vague prohibitions get argued with. Specific ones don’t. Microsoft’s own Copilot supplemental terms of use already ban a defined set of behaviors, and your internal policy should restate them in language your staff will actually read.

    Ban, without exception:

    • Generating content that supports illegal activity, including fraud or forged documents.
    • Doxing or attempting biometric identification of any individual.
    • Creating non-consensual deepfakes, image manipulation, or impersonation of a real person.
    • Producing disinformation, hate speech, or extremist material, even as a “test.”
    • Entering anything covered by attorney-client privilege, work product doctrine, or a signed NDA.

    The highest-risk moment isn’t the obvious violation. It’s the paralegal who pastes a settlement draft into Copilot Chat to “clean up the tone,” not realizing the tenant may retain that prompt. Redaction has to happen before the paste, not after.

    Pro Tip: Build a one-page “never paste this” card with three real (anonymized) examples from your own files. Abstract rules get ignored. A recognizable near-miss gets remembered.

    How Do You Set Data Rules for What Staff Can Input?

    Map your existing data classification tiers directly to Copilot permissions instead of inventing a parallel system. The University of Ottawa’s approach, and separate Microsoft Learn guidance on enterprise data protection, both point to the same principle: classification should drive machine access, not staff judgment alone.

    1. Public and internal-general data. Safe for summarization, drafting, and Q&A.
    2. Internal-sensitive data (unsigned contracts, internal financials). Allowed only in Copilot Chat with company data protection enabled, never in consumer Copilot.
    3. Confidential and client-privileged data. Excluded from Copilot entirely; route through an approved, access-controlled workflow instead.

    A before/after redaction example makes this concrete: “Summarize the deposition of John Smith regarding the Q3 fraud claim” becomes “Summarize the attached deposition regarding a Q3 financial dispute” with the file handled through a locked workspace, not pasted as text.

    Pro Tip: When a staff member isn’t sure which tier a document falls into, the rule is simple: don’t input it. Ask, or use the approved workflow. Guessing wrong here is how privilege gets waived.

    Which Tenant Settings Actually Enforce the Policy?

    Policy language without technical enforcement is a suggestion. Practitioner guidance on Copilot governance is blunt about why: automation bias means staff tend to trust AI outputs by default, so controls that depend purely on memory and good intentions fail more often than admins expect.

    Five settings do the real work:

    • Sensitivity labels with mandatory labeling so every document carries a machine-readable classification.
    • DLP rules blocking uploads of labeled confidential or privileged files into Copilot surfaces.
    • Knowledge and Graph exclusions removing sensitive SharePoint and Teams sites from Copilot’s indexed content.
    • Conditional access policies in Entra ID restricting Copilot use to managed devices.
    • Telemetry and retention settings capturing prompt-level usage for audit review.
    Control Risk it closes
    Sensitivity labels Unlabeled privileged files entering Copilot summaries
    DLP blocking rules Client-confidential document uploads
    Knowledge exclusions Copilot indexing restricted SharePoint sites
    Conditional access Unmanaged personal devices querying tenant data
    Telemetry logging Blind spots in high-risk prompt patterns

    Run this checklist quarterly, not once at rollout. Sensitivity labels drift as new document libraries get created, and nobody remembers to re-label them.

    How Should Training and Human Oversight Work?

    Training that isn’t tied to access is training nobody finishes. GitHub’s own responsible-use guidance for Copilot makes the same point in a different context: the tool should supplement judgment, never replace it, and that only holds if someone is actually reviewing outputs.

    1. Module one: what Copilot can and cannot see in your tenant.
    2. Module two: the prohibited-uses list, with real examples from your own practice area.
    3. Module three: human-in-the-loop checkpoints, specifically for client deliverables, legal filings, financial statements, or anything touching regulated advice.
    4. Attestation: a signed acknowledgment recorded in your HR or LMS system before Copilot access is provisioned, not after.

    Tie the attestation record directly to license assignment. If someone hasn’t signed off, they don’t get a seat. It’s a five-minute integration and it closes the single most common gap auditors find.

    How Long Should You Keep Copilot Chat Logs?

    University guidance treats most Copilot chats as transitory working material, not permanent records, and recommends saving only the final output in an approved repository.

    • Keep prompt and chat logs for a defined window purely for security review, not as a working archive.
    • Save finished deliverables, drafts, and any output used in client work in your document management system with normal version control.
    • Disclose Copilot involvement in formal documents where accuracy or authorship matters. A simple line, “This draft was prepared with AI assistance and reviewed by [name],” covers most cases.
    • For data subject access requests, treat retained prompt logs as discoverable records subject to your existing privacy obligations.

    Canadian government guidance on AI use in funded research reinforces the same expectation: transparency and audit trails matter whenever an AI-assisted output feeds a formal decision.

    What’s the Incident Response Plan for a Copilot Leak?

    Move fast, in a set order, before anyone starts guessing at causes.

    1. Isolate. Suspend the affected user’s Copilot access immediately, not at end of day.
    2. Preserve. Pull prompt logs and telemetry before retention windows roll over anything relevant.
    3. Notify internally. Loop in security and legal within hours, not after an internal investigation wraps.
    4. Assess client notification. If privileged or client data was exposed, your existing breach notification obligations apply the same way they would to any other data incident.
    5. Remediate. Revoke or restrict access, tighten the DLP rule that failed, and document what changed.
    6. Review. Run a post-incident debrief within a week and update the AUP if the gap was policy, not just enforcement.

    What Does a Copy-Ready Copilot Policy Clause Look Like?

    Legal will still need to review language for your jurisdiction, but starting from real clauses beats starting from a blank page.

    • Scope: “This policy governs all use of Microsoft 365 Copilot and Copilot Chat by employees, contractors, and temporary staff across [Firm Name]’s tenant.”
    • Permitted use: “Staff may use Copilot for drafting, summarization, and research support using data classified as Public or Internal-General.”
    • Prohibited use: “Staff shall not input client-privileged, highly confidential, or regulated personal data into any Copilot interface.”
    • Human review: “All Copilot-assisted content used in client deliverables, financial statements, or legal filings requires review and sign-off by a qualified staff member before distribution.”
    • Enforcement: “Violations may result in retraining, temporary suspension of Copilot access, or termination of license, at management’s discretion.”
    Role Allowed workflow Approval needed
    Associate/staff accountant Drafting, internal summarization Manager sign-off on client use
    Paralegal/analyst Research support, document formatting Attorney or senior reviewer
    Partner/principal Client communication drafts Self-review, logged
    IT administrator Tenant configuration, audit review None (policy owner role)

    Regulated practices (securities, healthcare-adjacent consulting) should add a jurisdiction-specific clause and keep legal review notes attached to the policy file, not buried in email.

    How Do You Roll Out and Enforce the Policy?

    Rollout works best in a sequence, not a single big-bang launch.

    1. Pilot with one team for two to four weeks while you set a telemetry baseline.
    2. Measure dormant licenses, high-risk prompt attempts blocked by DLP, and completion rate on training attestation.
    3. Expand in phases by department, tightening tenant controls as you go rather than loosening them.
    4. Set a review cadence (quarterly is standard) for the policy itself and the technical guardrails behind it.

    Track adoption rate, dormant license reduction, blocked high-risk prompts, incidents per quarter, and recoverable billable time as your core signals. A telemetry-based baseline is what turns “we think adoption is fine” into a number you can defend to a managing partner.

    Enforcement should escalate, not jump straight to termination: coaching conversation first, mandatory retraining second, temporary suspension third, full access revocation only after repeated or serious violations.

    Zera.ai’s Approach to Governance-First Copilot Adoption

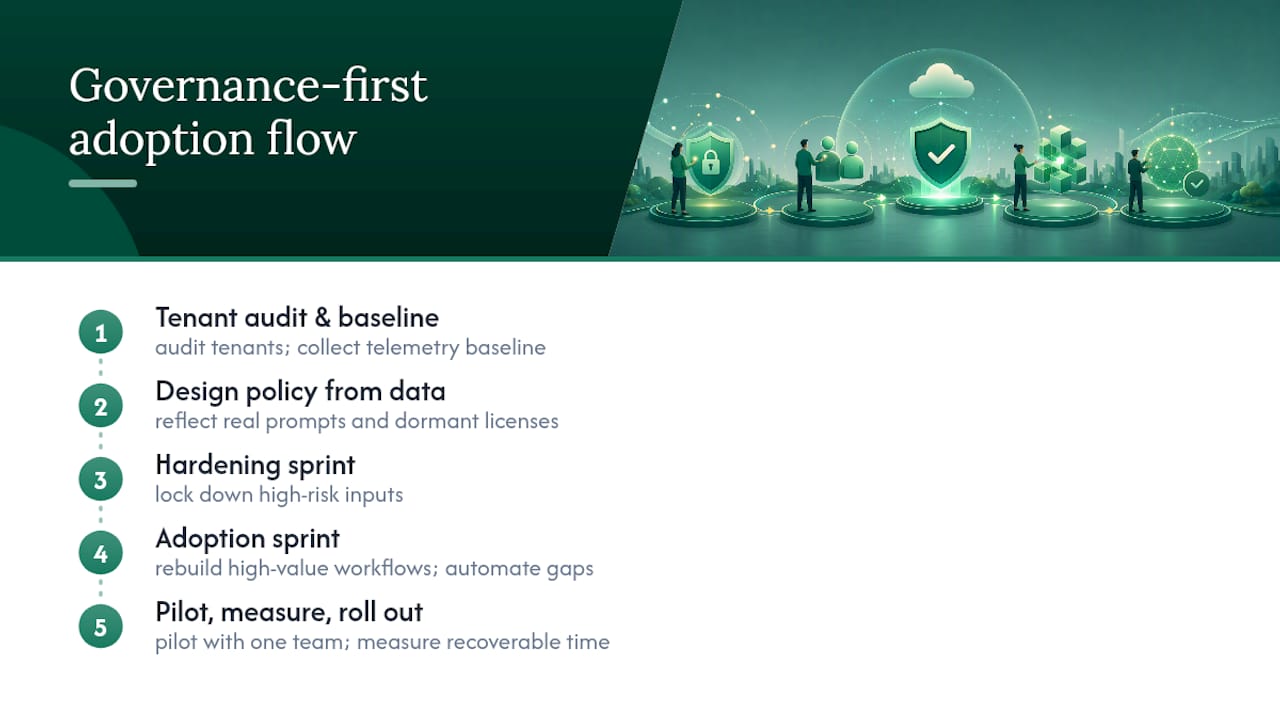
    Most AUPs fail quietly. They get written, filed, and ignored because nobody connects the policy to actual usage data. Engagements start with a tenant audit and telemetry baseline before touching a single clause, so the policy reflects real prompt patterns and dormant licenses rather than guesswork. From there, a targeted hardening sprint locks down high-risk inputs, followed by an adoption sprint that rebuilds high-value workflows and automates the gaps with available automation tools. A typical quick win is to pull the dormant-license list, pilot the policy with one advisory team, and measure recoverable billable time before rolling out firmwide.

    Zera.ai's Approach to Governance-First Copilot Adoption — overview diagram

    — Mad

    Sources

    Start with Microsoft’s Copilot supplemental terms of use, the University of Ottawa’s Copilot guidelines, the NHSmail M365 Copilot Acceptable Use Policy, and Government of Canada AI research guidance. Have legal counsel review any clause you adapt for your jurisdiction before publishing it firmwide, and consider a governance-first implementation approach if you’re building this from scratch rather than retrofitting an existing IT policy.

  • Cut Copilot Spend in 30–90 Days for Mid-Market Professional Services

    Cut Copilot Spend in 30–90 Days for Mid-Market Professional Services

    Cutting wasted Copilot spend comes down to three moves: measure who actually uses their license, reclaim the seats sitting dormant, and reassign the freed-up budget to roles where drafting, summarizing, and analysis happen daily. Firms that skip the measurement step almost always overspend, because unused $30 seats are invisible until someone pulls the usage report.


    TL;DR:

    • Focus pilot programs on high-value workflows like drafting, summarizing, and Excel analysis before scaling to gain quick ROI and build credibility.
    • Run a permissions audit to fix outdated sharing links, restrict sensitive file access, and ensure proper classification before expanding Copilot deployment.
    • Measure license efficiency using active user rates and prompts submitted, with automated APIs enabling weekly reporting to inform reallocations.
    • Calculate ROI by comparing time saved, billed rates, and billable days, aiming for workflows where time savings exceed license costs within a month.

    Table of Contents

    What Steps Optimize Copilot Spend This Quarter?

    You do not need a six-month change program to stop the bleeding. A tight 30 to 90 day push, run by IT with Ops handling communication, gets most of the waste out of the system.

    1. Pull the Copilot usage export and flag every license with zero activity in the reporting window.
    2. Notify license holders and run a transparent pause or reassign process, no surprise cutoffs.
    3. Launch a 2 to 6 week role-based pilot around three high-value workflows, not a company-wide rollout.
    4. Lock down oversharing on flagged sites and apply sensitivity labels where content is sensitive.
    5. Stand up a weekly adoption dashboard and a one-page executive ROI snapshot.
    6. Assign ownership clearly: IT owns measurement, Ops owns communication, partners set expectations with their teams.

    Pro Tip: Run the pilot on the three workflows with the most repetitive written output first, drafting templates, meeting summaries, client intake, before you touch anything else. That’s where the fastest, most visible ROI shows up, and it buys you credibility for the harder rollout decisions later.

    How Do You Measure Copilot Usage Reliably?

    Start in the Microsoft 365 admin center. The Copilot usage report shows Enabled Users, Active Users, Active User Rate, Prompts Submitted, and Adoption by App, and it exports to CSV, which matters when finance wants an audit trail. Data typically refreshes within 48 hours, so this is not a real-time feed, but it’s close enough for weekly decisions.

    A few definitions matter more than people assume:

    • Enabled users hold a license, whether or not they’ve opened the app.
    • Active users submitted at least one prompt in the reporting period.
    • Active user rate is the ratio between the two, and it’s the number that should drive your reclaim decisions.
    • Prompts per user and active days tell you whether use is habitual or a one-time curiosity click.

    For a strategic view across roles and time, the Copilot Dashboard inside the Copilot Control System pulls in Viva Insights data and lets you customize metrics against your own operational benchmarks, not just Microsoft’s defaults.

    If you want this automated instead of pulled manually every Friday, Microsoft Graph’s Copilot usage APIs return user-level detail, including last activity date and prompts submitted, which you can schedule into your own reporting pipeline. That single change turns license audits from a quarterly scramble into a standing report someone glances at every Monday.

    How Do You Reclaim Dormant Copilot Licenses Without Disrupting Teams?

    Set a dormancy threshold before you touch a single seat. Sixty days with zero prompts submitted is a reasonable line for most professional-services firms, tight enough to catch waste, loose enough to avoid punishing someone who was on parental leave or a slow month.

    1. Identify every license below the threshold using the usage export.
    2. Notify the license owner directly, explain why, and give them a short window to respond.
    3. Pause licenses with no response, don’t delete access outright.
    4. Reassign or re-provision the freed seat to a pilot workflow or a waitlisted team member.

    Log every action. Keep the exports. Offer a 30-day reactivation window for anyone who genuinely needs the seat back. Reclaiming licenses without this kind of paper trail is how firms lose staff trust fast, people assume IT is coming for their tools next, and adoption stalls everywhere else in the building.

    Where Does Copilot Actually Produce Billable-Time ROI?

    License spend only pays off when it lands on roles doing the same kind of writing over and over. That’s paralegals drafting motions, junior associates summarizing depositions, audit staff writing findings memos, and proposal teams assembling boilerplate-heavy documents. Practitioner analysis of professional-services deployments consistently points to drafting, meeting summarization, and Excel narrative generation as the workflows with the clearest payoff, far more than general-purpose chat use.

    The rollout sequence that works:

    • Pick the workflow first, not the department. “Meeting summaries for client-facing partners” beats “give Copilot to the litigation team.”
    • Time the task before Copilot touches it. You need a baseline, five timed samples of the same task with the same person is enough to get a usable average.
    • Run short, hands-on enablement sessions built around that specific task, not a generic product tour.
    • Name two or three champions per department who answer questions in real time instead of routing everything to IT.
    • Build sample prompt templates tied to the actual document types your teams produce, engagement letters, findings memos, client update emails.

    Pro Tip: Skip the “explore what Copilot can do” training session entirely. Show one associate cutting a 90 minute summary down to 20 minutes in a live demo, and the rest of the team asks for training on their own.

    What Governance Gaps Should You Fix Before Scaling Copilot?

    Copilot surfaces whatever it can access, which means permission debt you’ve ignored for years suddenly becomes visible and uncomfortable. Run a permissions audit before you expand beyond the pilot group.

    • Check for broken inheritance in SharePoint and Teams sites, old sharing links nobody remembers granting.
    • Find anonymous or “anyone with the link” shares and shut them down.
    • Review broad security groups, especially ones like “All Employees” that got attached to sensitive libraries years ago and never got trimmed.
    • Apply sensitivity labels and Microsoft Purview rules so Copilot cannot surface classified client files, HR records, or unfiled deal documents in a summary or search result.
    • Clean up overshared libraries as a precondition, not a follow-up, to any firm-wide rollout.

    This is also where a governance guide focused on document and permission hygiene is worth a read, since the same principles that keep AI tools from surfacing the wrong file apply directly to how Copilot indexes your firm’s content. Skipping this step is the single most common reason professional-services firms stall Copilot adoption after a promising pilot.

    How Do You Calculate Copilot ROI and Break-Even?

    Three numbers decide whether a license pays for itself: time saved per workflow, the billing rate of the person doing the work, and how many billable days a month that workflow actually runs. Forrester’s Total Economic Impact analysis frames license and implementation cost as a real, material line item, but finds it’s outweighed by measured productivity gains when firms actually define their use cases instead of deploying blind.

    The break-even formula is simple:

    (Minutes saved per user per day × billing rate × billable days per month) ≥ license cost per user per month

    A paralegal saving 20 minutes a day at a $150 billing rate, across 20 billable days, generates roughly $1,000 a month in recoverable time against a license that costs a fraction of that. That math is why targeting the right roles matters more than expanding seat count.

    Track these on a fixed cadence:

    • Weekly: adoption dashboard, active user rate by role.
    • Monthly: ROI check against the break-even formula.
    • Quarterly: executive review tying license spend to recovered billable time.

    A tool like Zera’s workflow tooling breakdown can help you track which integrations actually move these numbers instead of guessing.

    The Zera Perspective on Optimizing Copilot Spend

    Most firms treat Copilot licensing as a set-and-forget purchase, then wonder eighteen months later why adoption never climbed past 20%. An expert consulting firm’s view, shaped by experience with mid-market professional-services firms, is that the license itself was never the product. The workflow rebuild around it is.

    The Zera Perspective on Optimizing Copilot Spend — overview diagram

    Baseline telemetry comes first, always, before a single training session gets scheduled. From there, targeted pilots on two or three workflows, backed by automation built in Python and n8n for the gaps Copilot leaves behind, tend to move active-use rates faster than firm-wide rollouts ever do. The pattern that shows up repeatedly: dormant licenses drop first, then time recovered on priority workflows becomes measurable within weeks rather than quarters, and that evidence is what actually gets a managing partner comfortable approving the next phase.

    The mistake isn’t overspending on licenses. It’s underinvesting in the fifteen hours of workflow redesign that would have made those same licenses worth every dollar.

    — Mad

    Fixed-Price Copilot Audit: What Zera Delivers and How to Start

    A consulting firm runs an alternative to open-ended change management for firms trying to optimize Copilot spend, offering a fixed-price audit with a defined scope and a defined end date, not a retainer that drags on for a year while adoption stays flat.

    Gozera

    The engagement pulls your telemetry export, builds a dormant-license report, and identifies three priority workflows with a real ROI estimate attached to each one, drafting, summarization, analysis, whatever fits your practice mix. You walk away with a CSV export of current usage, a list of recommended seat actions, a pilot roadmap, and a time-to-value estimate you can bring straight to a partner meeting. No guessing at what a rollout should look like six months from now.

    Before requesting the audit, pull your current license count, your most recent usage export if you have one, and a short list of the two or three roles you suspect are getting the least value from their seats. Visit the Zera Copilot consulting page to request the audit and see what a fixed-price engagement looks like for a firm your size.

    Sources

  • Telemetry First Copilot Adoption vs Usage for Mid Market IT

    Telemetry First Copilot Adoption vs Usage for Mid Market IT

    Adoption tells you how many Microsoft 365 Copilot or GitHub Copilot licenses are switched on. Usage tells you how many people actually submitted a prompt and got something back. If you’re a mid-market IT leader trying to justify the license spend, stop watching enabled-user counts and start watching active-user rate alongside cohort progression, since that combination is what actually predicts recovered billable hours. Open the Microsoft 365 admin Copilot usage report or the GitHub Copilot usage metrics API first, not the invoice.


    TL;DR:

    • Tracking active-user rate alongside cohort progression better predicts ROI than simply monitoring enabled-user counts or total prompts submitted.
    • Usage metrics like prompt acceptance and recent activity filter out superficial engagement signals often mistaken for true adoption.
    • Developers’ progression through adoption phases correlates with significant increases in pull request volume, indicating higher actual productivity gains.
    • Reallocating dormant licenses and focusing pilots on specific workflows with measurable KPIs improves engagement and accelerates ROI realization.
    • Combining telemetry-based insights with targeted workflow rebuilds and automation drives meaningful billable-hour recovery and clarifies true tool value.

    Table of Contents

    Adoption vs Usage for Copilot: What Each Term Actually Measures

    Adoption and usage sound like synonyms in most vendor decks. In telemetry, they’re different questions entirely. Adoption asks: how many people have a Copilot license and could use it? Usage asks: how many of them did something intentional with it this week?

    Microsoft’s own reporting draws this line precisely. An Enabled User is anyone assigned a Copilot license. An Active User is someone who performed a deliberate action, most commonly submitting a prompt, inside a Copilot-enabled app during the reporting window. Divide active users by enabled users and you get the active-user rate, the single number that separates real adoption from shelfware.

    Here’s where most internal reporting goes wrong. Opening the Copilot pane, launching Word with Copilot visible in the ribbon, or signing into Teams does not count as an active action in Microsoft’s Copilot usage report. Only a submitted prompt, and in some cases an accepted suggestion, registers as usage. Firms that count pane opens as “adoption” routinely overstate engagement by a wide margin and miss the workflow friction actually stalling their rollout.

    A few measurement traps worth flagging for anyone building an internal dashboard:

    • Sign-in counts and app launches are not usage signals; they’re proximity signals.
    • Per-app adoption varies widely. A firm can show strong Copilot activity in Outlook while Word and Excel sit untouched.
    • “Prompts submitted” and “prompts accepted” are different metrics. A high submission count with a low acceptance rate usually points to a training gap, not a tool problem.
    • License counts pulled from procurement records rarely match enabled-user counts in the admin report, since provisioning timing differs.

    Get these definitions wrong at the start and every ROI number built on top of them is fiction.

    What Telemetry Fields Actually Predict Copilot ROI

    Six fields matter more than the rest, and most firms track maybe two of them. Here’s the working list IT teams should pull every reporting cycle:

    1. Enabled users — total licensed seats, the denominator for every adoption calculation.
    2. Active users — users who submitted at least one prompt in the period.
    3. Active-user rate — active divided by enabled; this is the number that belongs in the boardroom deck.
    4. Prompts submitted — raw engagement volume, useful for trend lines, weak on its own.
    5. Prompts accepted — the quality signal behind the volume; low acceptance with high submission usually means bad prompting habits, not a bad tool.
    6. Assisted hours / time saved — a derived estimate, built from feature usage patterns, that maps most directly to billable-hour recovery.

    For engineering and software teams running GitHub Copilot, add developer-specific metrics: PR throughput, time-to-merge, and lines-of-code deltas mapped against adoption phase. These matter because code-related productivity gains show up in cycle time long before they show up in a survey.

    Statistic Callout: Microsoft’s Copilot usage report typically becomes available within 48 hours of activity occurring, which means a weekly review cadence captures real signal without chasing same-day noise.

    On cadence and timeframe: pull data weekly for pilot monitoring, but report monthly to leadership. Weekly numbers swing too much with vacation schedules and single-team pushes to mean much on their own. When choosing a timeframe filter in the admin report, remember the user-level table populates from anyone licensed within the trailing 180 days, including people who left the program or never touched the tool. Filter for recent activity, not just license history, or you’ll understate the active-user rate without realizing it.

    Why Cohort Progression Matters More Than a Single Usage Number

    A 40% active-user rate tells you almost nothing about depth. Two firms can hit that same number, one with everyone lightly dabbling and one with a smaller group deeply embedded, and their ROI outcomes will look completely different. This is where cohort analysis earns its place in the reporting stack.

    GitHub’s Copilot usage metrics API classifies developers into four adoption cohorts: No cohort, Code first, Agent first, and Multi-agent. Assignment isn’t based on a single session. It follows a 2-day-in-28 engagement rule, meaning a developer needs activity on at least two separate days within a rolling 28-day window to land in a meaningful cohort at all. That threshold filters out one-off curiosity clicks and isolates people who’ve actually built the tool into their routine.

    Why this matters for ROI: progression between phases correlates with measurable output gains, not just survey sentiment. Analyzed datasets show developers moving from phase one to phase two produced roughly 78% more pull requests, and phase-one to phase-three progression showed gains near 151% more PRs in the same tracked cohorts. That’s not a rounding error. That’s the difference between a license that pays for itself and one that doesn’t.

    For non-developer teams, the same logic applies conceptually even without GitHub’s exact phase labels: track how many users go from occasional prompt submission to daily habitual use, and treat that migration as the metric to optimize.

    • No cohort: licensed but no meaningful engagement pattern.
    • Code first: uses Copilot primarily for inline code suggestions.
    • Agent first: relies on agent-mode workflows for larger tasks.
    • Multi-agent: coordinates multiple agent workflows, the deepest adoption tier.

    Pro Tip: Before buying more licenses, pull your cohort mix. If most of your active users sit in the lowest tier, the problem is enablement, not seat count, and more seats will just create more dormant licenses.

    How to Pull Adoption and Usage Numbers from Microsoft and GitHub

    Knowing the right metrics doesn’t help if you can’t find them. Here’s the practical path to each report.

    1. Microsoft 365 admin Copilot usage report. Sign into the Microsoft 365 admin center with global admin or reports-reader permissions, navigate to Reports, then Usage, and select the Microsoft 365 Copilot tab. You’ll see enabled users, active users, active-user rate, and a per-app breakdown showing which tools (Word, Excel, Teams, Outlook) drive activity.
    2. Viva Insights / Copilot Dashboard. This layer adds organizational context: usage trends by team or department, correlation with meeting load, and manager-level rollups the raw admin report doesn’t surface. Use it when leadership wants a narrative alongside the numbers, not just a table.
    3. GitHub Copilot usage metrics API. For engineering teams, query the API directly for fields like ai_adoption_phase and totals_by_ai_adoption_phase. The API beats the UI whenever you need to join Copilot data with your own PR or ticketing data, or when you’re reporting across dozens of repositories at once.
    4. Watch the denominator. The user-level table in the Microsoft admin report includes anyone licensed in the trailing 180 days, even people who’ve since had licenses revoked. Filter by recent activity date, not license status, before calculating your active-user rate.
    5. Confirm permissions before the reporting cycle starts. Reports-reader access differs from full admin access, and Viva Insights often requires a separate license tier. Sort this out ahead of your first board update, not during it.

    Timeframe selection matters more than people expect. A 7-day window flatters pilot teams and punishes slower-moving departments; a 90-day window smooths seasonal dips but hides recent momentum. Pull both when you’re building a business case.

    A Practical Framework for Turning Telemetry into ROI

    The translation from usage data to dollars follows a simple chain: feature usage becomes assisted minutes, assisted minutes become recoverable hours, recoverable hours become either billable revenue or a direct cost offset. The mistake most firms make is skipping straight from “people are using it” to a big ROI number without walking that chain explicitly.

    Build the calculation this way:

    • Start with active users in a given app, not enabled users.
    • Estimate assisted minutes per active user per week, based on feature usage patterns rather than self-reported guesses.
    • Convert assisted minutes to hours per month, then multiply by a blended billable rate (for law and accounting firms, this is usually the most defensible number in the model).
    • Apply a conservative discount, 20 to 30%, to account for time that would have been spent on the task anyway without Copilot.
    • Report a range, not a single figure, and flag your assumptions explicitly for finance.

    For a developer-focused example, tie the calculation to cohort progression instead of raw prompt counts.

    Statistic Callout: Forrester-style vendor research on Microsoft 365 Copilot cites faster time to market and operating-cost reductions for SMBs integrating Copilot into daily workflows, but treat vendor-commissioned figures as directional, not a substitute for your own telemetry-based model.

    For a full worked template, the ROI framework for mid-market firms walks through the billable-hour math step by step.

    How to Move Users from Trial to Daily, Productive Usage

    Enablement work is where the active-user rate actually moves. Generic training decks rarely change behavior. Specific, role-anchored pilots do.

    Start by designing pilots around a single role and a single measurable outcome, not the whole firm at once. A litigation support team piloting Copilot for deposition summaries needs a different success metric than an audit team piloting it for workpaper drafts. Set the KPI before the pilot starts, not after.

    Embed Copilot into the artifacts people already touch daily. Engagement letter templates, proposal skeletons, recurring client reports, these are where prompt habits stick. A generic “here’s what Copilot can do” slide deck rarely survives contact with a billable-hour culture; a prompt built directly into the firm’s engagement letter template does.

    • Set a 90-day KPI per pilot group before rollout, not after.
    • Build 2 to 3 high-frequency templates with prompts pre-loaded, rather than training on open-ended use cases.
    • Use telemetry to trigger nudges when a user’s last-activity date crosses a threshold, then measure reactivation over the following 28 days.
    • Reassign licenses sitting dormant for 90-plus days to new pilot participants instead of buying additional seats.
    • Scale the rollout only when a pilot group hits its stated KPI twice in a row; stop and redesign if it doesn’t.

    Pro Tip: Track prompt-to-deliverable conversion, not just prompt volume. A team submitting 500 prompts a month that produces 12 finished deliverables has a different problem than a team submitting 100 prompts that produces 40.

    What a Telemetry-First Consulting Engagement Actually Looks Like

    Some firms run this measurement work internally with success. Others don’t have the bandwidth, and that gap is exactly where a firm’s IT team should decide whether to bring in outside help.

    Gozera’s approach starts with a telemetry baseline: pulling actual usage data before recommending anything, rather than assuming licenses equal engagement. From there, the work identifies dormant licenses sitting unused for 90 days or more, rebuilds two or three high-frequency workflows around Copilot instead of leaving adoption to chance, and fills automation gaps with Python and n8n where Copilot alone can’t close the loop.

    The target outcome is recoverable billable time backed by a measurable ROI report, not a vague productivity claim.

    • Baseline telemetry audit against enabled-user and active-user data.
    • Dormant-license identification and reallocation planning.
    • Workflow rebuilds tied to specific templates and deliverables.
    • Automation layered on top using Python scripting and n8n workflows.
    • ROI reporting anchored to billable-hour recovery, reviewed on an ongoing basis.

    Engaging outside help makes the most sense when internal IT lacks the bandwidth to run a proper telemetry audit alongside daily operations, or when the firm needs an outcome report credible enough to bring to partners.

    My 90-Day Priority Checklist for IT Leaders

    If you’re inheriting a Copilot rollout that’s stalled, resist the urge to buy more licenses or run another training webinar. Fix the measurement first.

    Month zero through one: pull your baseline telemetry from the Microsoft 365 admin report, identify every license that’s gone dormant for 90 days, and reallocate two or three of them to a pilot group with a defined KPI. That’s your quick win, and it costs nothing extra.

    Month two through three: run targeted pilots around specific templates, not generic training. Recruit two or three champions per department and let their usage patterns, not their opinions, guide the rollout.

    By day 90, report three numbers to leadership: active-user rate change, cohort mix shift (if you’re tracking developer usage), and an estimated hours-recovered figure with your assumptions attached. Skip the vanity metrics. Nobody upstairs cares how many licenses are enabled if the active-user rate hasn’t moved.

    — Mad

    Get an Outside Audit of Your Copilot Usage Gap

    Gozera exists for the exact problem this article walks through: firms paying for hundreds of Copilot seats while active-user rate sits in the single digits. Where a generic training vendor sells a workshop and moves on, Gozera runs a telemetry-first audit, finds the dormant licenses actually draining your budget, and rebuilds two or three real workflows so the tool sees daily use instead of quarterly curiosity.

    Gozera

    Engagements scale to the problem. A standalone audit maps your current enabled-versus-active gap and dormant-license count. An integration sprint rebuilds specific high-frequency workflows, like engagement letters or recurring client reports, around Copilot with automation support where needed. A monthly retainer keeps the ROI reporting current as usage patterns shift. This fits mid-market law, accounting, consulting, and engineering firms in the 50 to 500 employee range specifically, where a handful of workflow rebuilds move the active-user rate more than a firm-wide license refresh ever would. Explore the Copilot adoption consulting services Gozera offers and book a baseline audit to see where your dormant licenses are actually sitting.

    Primary Sources for Pulling Your Own Numbers

    Sources

  • Seven Pillars to Prove Copilot Readiness for Mid Market Firms

    Seven Pillars to Prove Copilot Readiness for Mid Market Firms

    Most mid-market firms are not ready for Microsoft 365 Copilot, and the gap almost always comes down to permissions and licensing, not the AI itself. A proper copilot readiness assessment ends with three things: a prioritized fix list, a pilot plan, and measurable ROI targets. The immediate next step is simple. Run the Microsoft Copilot Readiness report in the admin center or an automated tenant scan today, before you assign another license.


    TL;DR:

    • Most firms are held back by permissions and licensing issues, not the AI capabilities, making readiness assessments crucial before deployment.
    • Ensuring all users have the correct licenses, accounts are in Exchange Online, and network endpoints are unblocked is essential for a smooth Copilot experience.
    • Permissions and content hygiene heavily influence Copilot’s answer quality, as it only surfaces content users can already access through existing permissions.
    • Automated scans using APIs from Graph, Defender XDR, and Purview provide faster, more objective readiness evaluations than manual checklists.
    • Effective pilots require deliberate task-based measurements, involving both enthusiastic and skeptical users, to generate meaningful usage data and ROI.

    Table of Contents

    What Are the Minimum Technical Prerequisites for Copilot?

    Copilot has non-negotiable technical gates, and missing any one of them produces a degraded or broken experience rather than a clean failure. That’s worse than an outright block, because users blame the AI when the real problem is infrastructure.

    Microsoft’s own documentation lays out the baseline clearly. Every user needs a qualifying Microsoft 365 base plan and a Copilot add-on license, plus a handful of identity and mailbox conditions that get overlooked constantly during rollout planning.

    • A qualifying Microsoft 365 or Office 365 base plan (E3/E5, Business Standard/Premium, or equivalent) with the Copilot add-on assigned.
    • A primary mailbox hosted in Exchange Online. Hybrid or on-premises mailboxes silently degrade grounding.
    • An active Microsoft Entra ID account tied to the tenant.
    • A supported client on a current update channel, meeting minimum desktop OS, browser, and mobile OS versions.
    • Unblocked network endpoints for Copilot and Microsoft Graph traffic.

    Firms mid-migration to Exchange Online are the most common failure case. Users technically hold a license, but their mailbox sits on-premises, so Copilot can’t ground responses in their email or calendar history. The result looks like a bad product. It’s actually a sequencing problem, and it’s why pilot users should be pulled from tenants already fully migrated, not from whichever department volunteers first.

    How Does the Semantic Index Affect Copilot’s Answers?

    Copilot’s answer quality depends almost entirely on what it can see, not on the model behind it. Microsoft builds a tenant-level semantic index for Copilot from SharePoint Online content, and that index, combined with Microsoft Graph, is what grounds a response in your actual documents, emails, and chats instead of generic training data.

    The permission model is the part IT teams underestimate. Copilot only surfaces content a user can already access through their existing SharePoint and OneDrive permissions. It doesn’t grant new access. That sounds safe, but it means years of oversharing (link-shared folders, “everyone” groups, stale project sites) turn into instantly discoverable answers the moment Copilot goes live.

    Pro Tip: If a partner at your firm has never audited who can open a client folder, assume Copilot will find and surface it. Grounding exposes bad permission hygiene faster than any manual audit ever did.

    Well-tagged libraries and consistent metadata improve scoped query results measurably, since the index can match intent to content more precisely. Admins have real levers to pull here: sensitivity labels, Restricted Content Discovery to exclude specific sites, Purview DLP policies, and IRM protections, though IRM-protected files carry their own indexing caveats worth testing before rollout. Microsoft confirms that semantic indexing does not train foundation models on your content and stays inside your tenant boundary, which matters when legal asks the obvious question.

    Semantic index filtering authorized content

    Building a Reproducible Readiness Scoring Model

    A copilot readiness checklist only earns its keep if it produces a number someone can act on, not just a pile of observations. The most useful models score across seven pillars and map the total to a rollout decision.

    1. Licensing — Percentage of intended pilot users with a qualifying base plan and Copilot add-on assigned.
    2. Identity & access — Entra ID hygiene, conditional access coverage, and multifactor enforcement.
    3. Permissions & content — Rate of overshared sites, orphaned permissions, and external sharing links.
    4. Purview & DLP — Sensitivity label coverage and active DLP policies on regulated content types.
    5. Security posture — Defender findings tied to identity and endpoint risk.
    6. Power Platform governance — Environment strategy and data loss prevention policies for connected apps.
    7. Adoption & telemetry — Baseline usage data and a plan to capture it during pilot.

    Readiness scorecards commonly weight these pillars and translate the total into four tiers: Not Ready, Pilot Only, Controlled Rollout, and Strong Readiness. A firm scoring low on permissions but strong everywhere else typically lands in Pilot Only. A firm with clean identity and content controls but no telemetry plan still can’t justify Controlled Rollout, because nobody will be able to prove the ROI afterward.

    Each pillar needs a pass or fail check with evidence you can export to CSV or Excel, not a gut feeling from the IT director. Reassess quarterly, and report the delta to managing partners in the same format each time, so a shrinking overshare count or rising license utilization rate becomes a visible trend rather than a one-off snapshot.

    Should You Automate the Assessment or Run It Manually?

    Automated, API-driven scans beat manual checklists on every dimension that matters to a governance committee: speed, objectivity, and reproducibility. Microsoft’s own automated readiness assessment tool pulls from Graph, Defender XDR, and Purview to analyze licensing, identity, permissions, and Power Platform governance in one pass, then exports a timestamped report.

    • Microsoft Graph for license assignment and identity data.
    • Defender XDR for security posture and risk signals.
    • Purview DLP for sensitivity labels and policy coverage.
    • Copilot admin APIs for readiness and usage metrics.

    A practical setup runs a PowerShell or Python orchestrator that calls each API in sequence, normalizes the output, and writes a dated CSV or Excel file. Pro Tip: Keep every scan output. A timestamped trail is what lets you prove remediation actually worked, instead of just asserting it in a slide.

    Manual review still matters for anything contextual: judging whether a shared client folder should stay open, or whether a department’s workflow justifies an exception. Automation finds the problems; humans still decide the policy.

    How Do You Design a Pilot That Produces Real Signal?

    A pilot that just hands out licenses and waits produces almost no usable data. Effective pilots need structure from day one, borrowing from Microsoft’s own adoption planning checklist, which recommends an executive sponsor, a mix of enthusiasts and skeptics, and task-based measurement rather than open-ended exploration.

    1. Pick departments deliberately. Include at least one group likely to resist, not just your most enthusiastic team. Skeptics surface friction that champions miss.
    2. Assign 2 to 3 measurable tasks per group. Meeting summaries, first-draft client deliverables, or email triage work well because they’re easy to time before and after.
    3. Track a defined KPI set: active users, weekly retention, time saved per task, and license-to-active-user conversion.
    4. Pull telemetry from Teams, Outlook, and Word, not self-reported surveys.
    5. Review the Readiness and Usage tabs weekly. The Copilot readiness report covers a rolling 28-day window and flags a quarter of nonlicensed users as suggested candidates, though the dashboard can lag up to 72 hours.

    Export the CSV each week and compare cohorts, not just aggregate numbers. A department stuck at low retention after week three is telling you something training alone won’t fix.

    What Should You Fix First, and How Long Does It Take?

    Remediation has a natural order, and skipping ahead wastes effort. Fix the fast, mechanical items first; save the slow, political ones for later.

    • Priority 1, days not weeks: Correct license assignments and confirm every pilot user’s mailbox sits in Exchange Online. This is a data cleanup task, not a project.
    • Priority 2, one to three weeks: Find, contain, remediate. Run a Purview data risk assessment to locate overshared sites, apply Restricted Content Discovery to keep them out of Copilot immediately, then fix ownership and inheritance underneath.
    • Priority 3, four to eight weeks: Sensitivity labels and DLP policy rollout. This needs business input from legal and practice leads, so build in review time rather than treating it as an IT-only task.

    Pro Tip: Contain before you rewrite. Applying site-level exclusions while you sort out permissions is faster and safer than attempting a wholesale permission overhaul before you actually know where the damage is.

    Re-run the automated scan after each priority tier closes. Improved grounding quality and rising pilot adoption are your two honest signals that remediation worked.

    A Data-Driven Way to Turn an Assessment Into ROI

    An assessment only earns its cost if it changes what happens next. Gozera’s approach starts with baseline telemetry, identifies dormant licenses draining budget, rebuilds the two or three workflows that actually matter to billable work, and closes remaining gaps with targeted automation using Python and n8n.

    • Baseline usage measurement before touching a single workflow.
    • Dormant license identification tied to real cost recovery.
    • Workflow rebuilds around high-value, repeatable tasks.
    • ROI reporting that maps directly back to the readiness score.

    DIY works when governance gaps are minor and someone internal has bandwidth. A consultancy earns its fee when governance is genuinely messy or leadership needs measurable ROI on a fixed timeline.

    The Overlooked Truth About Readiness Scores

    The conventional advice treats a copilot readiness assessment like a compliance gate: pass it, deploy, move on. That framing misses the point entirely. A high score on licensing and identity hygiene tells you almost nothing about whether Copilot will generate recoverable billable hours at a law firm or an engineering practice. Those are two separate questions, and most vendors collapse them into one report because a single number is easier to sell.

    Separate technical and business value tracks

    What the research actually supports is a two-stage view. Technical readiness (licensing, Entra ID, mailbox placement, permissions) is a gate you either clear or you don’t. Adoption readiness (whether a mixed pilot group of skeptics and enthusiasts produces measurable time savings on real tasks) is a separate, ongoing measurement problem that never fully closes. Firms that treat the second stage as an afterthought end up with a clean readiness score and a stack of idle licenses six months later.

    Prioritize the boring stuff first: mailbox migration, permission cleanup, sensitivity labels. Then measure adoption like you’d measure any other operational change, with real telemetry, not survey sentiment. The score gets you in the door. It doesn’t buy you the ROI.

    — Mad

    Ready to Turn Your Readiness Score Into Measurable ROI?

    Gozera is the alternative to guessing whether your Copilot investment is working: instead of a generic checklist, you get a data-driven scan that traces licenses, permissions, and usage to actual billable-hour recovery for professional-services firms.

    Gozera

    The engagement covers a full tenant scan, a prioritized remediation plan mapped to the pillars above, a pilot design built around your practice groups, and ROI reporting that tracks time saved against license cost. Gozera also builds on findings from a detailed Copilot license audit and telemetry instrumentation work already published for IT managers running similar rollouts. Firms comparing tooling ecosystems for their broader AI stack can also look at partners like Prowl for market-intelligence tooling that complements a Copilot deployment.

    Request a scoping call at Gozera to get a sample deliverable and a straight answer on where your firm actually stands before you renew another batch of Copilot licenses.

    Sources

  • Recover Billable Hours in 90 Days with an AI CoE for Mid Market Firms

    Recover Billable Hours in 90 Days with an AI CoE for Mid Market Firms

    An AI Center of Excellence (AI CoE) is the internal team that owns AI strategy, governance, and reusable infrastructure so adoption doesn’t happen ad hoc across departments. The single best first move is securing an executive sponsor and drafting a charter that names the mission, decision rights, and the first three metrics you’ll report on. Everything else, staffing, operating model, tooling, follows from that one decision.


    TL;DR:

    • Establishing an AI CoE requires securing executive sponsorship and drafting a clear charter focused on mission, decision rights, and initial metrics.
    • Staffing should include an executive sponsor, AI strategy lead, technical specialists, and legal or compliance reps to ensure balanced oversight and effective deployment.
    • Transition from centralized control to an advisory model gradually, with a focus on embedding standards in workflows and maintaining oversight for high-risk use cases.
    • Early pilot projects should focus on automating routine workflows with measurable before-and-after impact, avoiding high-complexity or uncertain-use cases initially.
    • Measuring license utilization and active adoption is crucial, as low engagement indicates workflow issues that need fixing before governance or strategic scaling.

    Table of Contents

    What Is an AI Center of Excellence?

    An AI CoE is the group inside your organization responsible for turning scattered AI experiments into a governed, repeatable capability. IBM defines it as a hub for expertise, governance, and best practices that aligns AI initiatives with strategic goals, and that definition holds up in practice.

    The core functions are consistent across industries: set the AI strategy, prioritize which use cases get built first, establish governance and risk controls, standardize data practices, build reusable assets, and measure business impact. Microsoft’s Cloud Adoption Framework frames the CoE as the mechanism that prevents fragmented, ungoverned AI adoption, where every department buys its own tool and nobody tracks results.

    Six connected AI CoE core functions

    Without a CoE, you get shadow AI: employees pasting client data into consumer chatbots, teams duplicating the same automation five different ways, and IT discovering a new AI vendor contract during the annual budget review. The CoE closes that gap by giving strategy a delivery mechanism.

    Why Build an AI Center of Excellence Now?

    The business case isn’t theoretical anymore. A 2024 industry observation cited by AWS found that 37% of large US companies have already established an AI/ML Center of Excellence, and that number keeps climbing as boards ask harder questions about AI spend.

    A CoE typically delivers on four fronts:

    • Faster time from pilot to production because teams reuse vetted templates instead of rebuilding governance from scratch
    • Lower compliance risk through consistent data handling, access controls, and audit trails
    • Reduced duplicate spend when departments stop buying overlapping tools independently
    • Clearer ROI reporting tied to specific business outcomes rather than license counts

    Pro Tip: Track cost-per-automated-task alongside license utilization from day one. A firm paying for 200 Copilot seats but seeing active use in only 60 has a utilization problem, not an AI strategy problem, and that distinction changes what you fix first.

    For a professional-services firm with 50 to 500 employees, the fastest proof point usually isn’t a flashy generative AI pilot. It’s recovering billable hours lost to manual drafting, document review, and status reporting, work Copilot already touches every day if it’s configured and adopted correctly.

    Why Build an AI Center of Excellence Now? — overview diagram

    Who Should Sit on the AI Center of Excellence Team?

    Staffing a CoE doesn’t require a dozen new hires. Most mid-market firms run lean, cross-functional teams pulled from existing staff plus a few targeted additions.

    • Executive sponsor: A managing partner or C-level leader who unblocks budget and resolves cross-department disputes; without this role, the CoE has no teeth.
    • AI strategy lead: Owns the roadmap, prioritizes use cases, and reports outcomes to leadership.
    • Data and platform specialists: Handle data quality, integration, and the technical plumbing behind any automation (this is often where Python and workflow tools like n8n enter the picture).
    • Security and compliance representative: Reviews data handling, access controls, and regulatory exposure before anything touches client data.
    • Legal counsel or risk officer: Especially critical for law and accounting firms handling privileged or regulated information.
    • Business champions: Practice-area leads who translate technical capability into workflows people actually use, and who catch adoption friction early.

    Skip any of these roles and you’ll find out the hard way. Firms that launch without legal or compliance involvement tend to discover data-handling problems only after a client asks pointed questions.

    Centralized, Federated, or Hybrid: Which Operating Model Fits?

    Responsibilities split into a few consistent buckets regardless of model: governance and risk, platform and infrastructure, use-case intake and prioritization, and training. How you distribute those buckets across the organization determines whether you’re running a centralized, federated, or hybrid CoE.

    • Centralized: One team owns everything, strategy, platform, and delivery. Works best for firms under roughly 150 employees or those just starting out, since it keeps governance tight while nobody has built local AI muscle yet.
    • Federated: Practice groups run their own AI projects, but the central CoE sets standards, approves risk thresholds, and provides shared infrastructure. Fits larger firms with distinct practice areas (say, litigation versus transactional law) that need different workflows.
    • Hybrid: Central team owns governance and platform; delivery teams embedded in each department own execution. This is where most firms land within 18 to 24 months, because pure centralization becomes a bottleneck once demand outpaces the CoE’s bandwidth.

    Responsibilities evolve as maturity increases. A firm two years into its AI program should be pushing more delivery authority to business units while keeping governance, security review, and KPI tracking centralized. Trying to centralize everything indefinitely usually produces a backlog nobody’s happy with.

    How Do You Structure an AI Governance Committee Charter?

    A governance committee is what turns “we have AI principles” into something an auditor can actually verify. Neither ISO 42001 nor the EU AI Act names a specific committee structure, but both require demonstrable accountability, and a chartered committee is the most efficient way organizations satisfy that requirement, a point reinforced by adoption research tying executive sponsorship directly to program success.

    A working charter should specify:

    1. Authority and scope: What the committee can approve versus what escalates to the board
    2. Membership and quorum: Permanent seats (legal, security, IT, a business unit lead) plus rotating members for specific reviews
    3. Meeting cadence: Monthly is typical for active programs; quarterly for mature, stable ones
    4. KPIs the committee tracks: Adoption rate, incident count, model performance drift, cost per use case
    5. Escalation thresholds: What risk level or spend amount triggers mandatory committee review before launch

    Aona AI’s committee charter template offers a ready structure covering membership, authority, and KPIs that firms can adapt rather than build from scratch. University governance models offer a useful parallel too: the University of Washington’s AI governance committee was built specifically to define human oversight and transparency policies, which is close to what a mid-market firm needs for client-data handling.

    Pro Tip: Document every committee decision, even the “no” decisions, with a one-line rationale. Auditors and regulators care less about what you approved and more about whether you can show you had a consistent process for evaluating risk.

    How Do You Build an AI Center of Excellence Step by Step?

    The first 90 days should focus on foundations, not features. Here’s a realistic sequence:

    Days 1 to 30:

    1. Secure an executive sponsor and get budget authority in writing
    2. Draft the charter (mission, scope, decision rights) and get it signed
    3. Inventory every AI tool already in use, including shadow deployments nobody officially approved
    4. Stand up the governance committee with at least legal, IT, and one business unit represented

    Days 30 to 90:
    5. Build an intake form scoring use cases on business value versus implementation complexity
    6. Select two or three pilot use cases that score high on value and low on complexity
    7. Run pilots with defined success criteria set before launch, not after

    Months 4 to 12:
    8. Move successful pilots to production with governance controls embedded, not bolted on afterward
    9. Publish a 90-day results summary to leadership showing adoption numbers and early ROI
    10. Expand intake to a second wave of use cases and start building reusable templates

    Enterprise playbooks consistently recommend classifying risk early and building reusable MLOps templates so pilots don’t stall in a governance review that should have happened before the pilot even started.

    Watch for these traps:

    • Picking pilots that are technically interesting but have no clear business sponsor
    • Skipping the intake criteria and letting the loudest department jump the queue
    • Declaring success without a baseline measurement to compare against

    Pro Tip: Your first pilot should be boring. Pick the use case with the clearest before/after metric, hours saved on a specific task, not the one that sounds most impressive in a board deck.

    What Technology Stack Should the CoE Provide?

    The CoE doesn’t need to build every tool itself, but it should own the standards everyone else builds against.

    • Reference architectures: A documented pattern for how retrieval-augmented generation (RAG), model access, and data pipelines connect, so every team isn’t reinventing plumbing
    • A shared model and use-case catalog: A living inventory of what’s approved, what’s in pilot, and what’s retired
    • MLOps and monitoring: Tooling to track model performance, drift, and failure rates over time
    • Access controls and data guardrails: Role-based permissions so sensitive client data never flows into an unapproved tool
    • Cost tracking with showback or chargeback: Visibility into which department is driving AI spend, tied back to the value it’s generating

    For firms already running Microsoft 365, this often means governing Copilot access alongside any custom automation built with tools like Python or workflow platforms such as n8n, rather than treating them as separate systems with separate rules.

    How Do You Measure Whether the CoE Is Working?

    KPIs split into two categories: technical health and business outcome. Track both, because a technically flawless pilot that nobody uses is still a failure.

    • Adoption rate: Percentage of licensed users actively engaging with the tool weekly, not just logged in
    • Time-to-production: How long it takes a use case to move from pilot to live deployment
    • Cost-per-inference or cost-per-task: What each automated action actually costs versus the manual alternative
    • Model quality and drift: Whether output accuracy holds steady over time
    • Business outcome metrics: Hours recovered, error rates reduced, client turnaround time improved

    The 37% adoption figure for large-company AI CoEs cited by AWS is a useful benchmark, but the number that actually matters to your board is your own baseline. Measure license utilization and task-level telemetry before you launch anything new, so the “after” number means something.

    Report to executives monthly during the first year, then shift to quarterly once the program stabilizes. A one-page dashboard showing adoption trend, top three use cases by ROI, and open risk items beats a 40-slide deck every time.

    When Should the CoE Shift From Control to Advisory?

    Centralized control makes sense early because nobody else has built the muscle to manage AI risk yet. That changes as practice groups build their own literacy and track record.

    Microsoft’s Cloud Adoption Framework recommends shifting from centralized control to an advisory model once business units demonstrate consistent, compliant delivery on their own. The signals to watch: pilots consistently passing governance review on the first submission, business units requesting fewer hands-on interventions, and incident rates staying flat even as usage grows.

    The transition itself should be gradual. Start by embedding CoE-approved standards directly into platform teams’ existing workflows, so compliance becomes default behavior rather than a separate checkpoint. Keep the governance committee’s review authority intact for high-risk use cases (anything touching client-privileged data or regulated decisions) even after delivery authority moves outward. Auditability doesn’t disappear just because control does. It just moves from manual review to automated guardrails and periodic spot checks.

    What Templates and Next Steps Should You Use First?

    You don’t need to build every artifact from scratch. A governance charter template, an intake scoring form, and a one-page pilot checklist cover most of what a new CoE needs in its first quarter.

    Three starter projects tend to prove ROI fastest for professional-services firms: automating a recurring status report, streamlining first-pass document review, and cleaning up meeting-to-action-item workflows. Each has a clear before/after time metric that’s easy to defend to a partner group skeptical of AI spend.

    For governance grounding beyond the charter itself, ISO 42001 compliance guidance offers a practical framework for aligning CoE policies with recognized management-system standards, useful groundwork before your first audit ever happens.

    Gozera’s Approach to AI CoEs for Professional-Services Firms

    Most AI CoE advice is written for enterprises with dedicated data science teams. Mid-market law, accounting, and consulting firms don’t have that luxury, and they shouldn’t try to copy that playbook wholesale.

    Gozera’s approach starts narrower: measure actual Copilot usage through telemetry before building anything new. We routinely find firms with dozens of dormant licenses sitting alongside teams that never got workflow support to use the tool well. That gap, not a lack of AI strategy, is usually the first problem worth solving. Our Copilot playbook for governance walks through how mid-market firms structure oversight without hiring a compliance department.

    A typical 90-day engagement starts with a usage audit and license utilization baseline, moves into rebuilding two or three high-value workflows around Copilot, and closes with automation (often built with Python or n8n) to handle the gaps Copilot can’t close alone. The deliverable partners care about isn’t a strategy deck. It’s recovered billable hours and a dashboard showing exactly where they came from.

    If your firm has more Copilot seats than active users, that’s the CoE conversation worth having first. Talk to Gozera about a Copilot ROI audit built for firms your size.

    The Part Nobody Tells You About AI CoEs

    Most AI CoE guidance treats governance and adoption as sequential: build the committee, write the charter, then worry about whether anyone actually uses the thing. That order is backwards for mid-market firms, and following it is why so many CoEs stall out after an impressive launch memo.

    Here’s the uncomfortable truth: a law firm with 150 employees doesn’t have the luxury of a six-month governance runway before showing results. Partners want to see recovered hours or reduced errors within a quarter, not a well-documented risk framework. That doesn’t mean skip governance. It means run adoption measurement and governance design in parallel, with the same urgency, instead of treating governance as the prerequisite that delays everything else.

    The other thing the standard playbooks underweight: license utilization is a leading indicator of CoE health, not a side metric. If half your Copilot seats sit idle six months after rollout, no charter or committee cadence will fix that. The problem is workflow integration, not oversight. Fix utilization first. Governance sticks better once people are actually using the tool you’re governing.

    — Mad

    Sources

  • 6 Copilot Workflows That Save Time for Mid Market Accounting Teams

    6 Copilot Workflows That Save Time for Mid Market Accounting Teams

    Copilot for accounting works best as a productivity layer inside tools your team already uses: Excel, Outlook, Teams, and, through Finance Agent, your ERP. It won’t close your books or replace a CPA’s sign-off, but it will cut hours off reconciliation, variance write-ups, and collections outreach when paired with human review. The fastest path to value is a single pilot, not a firmwide rollout: pick one recurring workflow, like bank reconciliation or AR follow-ups, and test one prompt against a real (but isolated) dataset this week.


    TL;DR:

    • Using Copilot for reconciliation can save hours by matching bank statements with general ledger data and flagging exceptions for manual review.
    • Effective prompts require specifying objectives, frameworks, periods, and audiences to produce useful, actionable outputs without heavy rework.
    • Governance measures, including data controls and human review checkpoints, are essential for CPA compliance and protecting client information during AI-assisted workflows.
    • Rollout success depends on measuring baseline processes, identifying idle licenses, and automating workflows, with a focus on re-billable time recovery.
    • Most firms discover unused licenses and fragmented data after initial implementation, making telemetry analysis vital to maximizing ROI and adoption.

    Table of Contents

    Top Copilot Use Cases for Accounting and Finance Teams

    The tasks that eat the most staff hours also happen to be the ones Copilot handles well, because they follow patterns: pull data, compare it, flag exceptions, write a summary. Here’s where mid-market accounting and finance teams see the fastest returns.

    • Reconciliation and bank statement matching. Feed Copilot an Excel export of the bank statement and the general ledger extract; it returns a matched summary and a flagged exception list for manual review.
    • Variance and trend analysis. Ask for a month-over-month comparison against budget, and Copilot drafts both the chart and a plain-language explanation of what moved and why, as well as strategies covered in Month End Close Automation: Cut Days Off Your Close.
    • Accounts receivable collections. Copilot ranks overdue accounts by risk and age, drafts outreach emails, and can suggest payment plan language based on account history.
    • Accounting document evaluation and standards updates. When a standard changes, Copilot can summarize requirements, locate affected documents, and draft the necessary edits, a workflow Microsoft’s own adoption scenario library walks through step by step.
    • Technical memos and audit narratives. Give it the facts and the audience, and it produces a first draft of a technical memo or client communication in the right tone and format.
    • Meeting recaps and action items. Pulled directly from Teams calls or Outlook threads, so nothing said in a client call gets lost by Thursday.

    None of these replace judgment. They replace the blank page and the first hour of manual data-wrangling that usually precedes it.

    How Does Copilot Integrate With Microsoft 365 and Finance Systems?

    Microsoft Copilot for Finance is the role-specific layer built for this exact job. It connects to Dynamics 365 and SAP and surfaces workflow automation and recommendations directly inside Outlook, Excel, and Teams, rather than living in a separate app your team has to remember to open.

    The specific component doing ERP work is Finance Agent. It acts as a query layer over your invoice and payment data, and it lets finance staff ask natural-language questions about AR and AP status directly inside Copilot chat instead of running a report and exporting it. Behind the scenes, Finance Agent and similar tools increasingly rely on the Model Context Protocol (MCP), an emerging standard for connecting AI assistants to external data sources and systems without custom integration work for every connector.

    Not every Copilot experience is the same one, though, and this distinction trips up a lot of firms during rollout:

    • Copilot Chat is the general-purpose assistant, useful for drafting and summarizing but with limited direct access to your line-of-business systems.
    • Microsoft 365 Copilot adds in-document actions inside Word, Excel, and Outlook, with broader tenant data access governed by your existing permissions.
    • Finance Agent sits on top of either, purpose-built for ERP queries, and often requires separate licensing.

    One licensing detail firms miss: Finance Agent and some Copilot for Finance capabilities may require additional licenses and admin-level tenant configuration beyond a standard Microsoft 365 Copilot seat. Confirm exact availability with Microsoft or your reseller before promising the capability to a partner or client, since role-based permissions also determine what each employee’s Copilot can actually see.

    Practical Workflows and Example Prompts for Common Accounting Tasks

    A good Copilot prompt for accounting work needs four things almost every time: the objective, the accounting framework, the period, and the intended audience. Skip any one of those and you tend to get a generic answer that sounds confident and says nothing useful. Here are six recipes worth keeping on hand.

    1. Bank reconciliation. Input: bank statement CSV plus GL extract. Prompt: “Match these two extracts by date and amount, list unmatched items over $500, and flag likely timing differences.” Output: a matched summary and a short exception list.
    2. Variance analysis. Input: actuals vs. budget by account. Prompt: “Compare actuals to budget for Q1 2026 under U.S. GAAP, flag variances over a $10,000 materiality threshold, and explain the top three drivers in plain language for a non-finance partner.” Output: a written variance narrative plus a chart.
    3. Accounting document update. Input: the policy document and the new standard summary. Prompt: “Summarize what changed in this standard, identify which sections of our policy document need edits, and draft the revised language.” Output: tracked-change suggestions.
    4. Collections email sequence. Input: AR aging report. Prompt: “Rank accounts over 60 days by balance, and draft a three-email escalation sequence, professional tone, for the top ten.” Output: prioritized list plus draft emails.
    5. Monthly close summary. Input: close checklist status and key metrics. Prompt: “Summarize close progress for the controller, flag open items, and estimate days to complete.” Output: a status memo.
    6. Board or partner-ready executive summary. Input: financial statements and prior period comparison. Prompt: “Draft a one-page summary for managing partners, focused on cash position and margin trend, no jargon.” Output: an executive brief.

    Pro Tip: Start a new Copilot conversation for each distinct task. Long threads that mix reconciliation questions with drafting requests tend to drift, and Copilot starts pulling context from the wrong task.

    Always name the framework (IFRS or U.S. GAAP), the exact period, and a materiality threshold in the prompt itself. Vague context is the single most common reason accounting professionals get outputs that need heavy rework.

    What Are the Risks and Governance Requirements for CPAs?

    Copilot drafts. It does not exercise professional skepticism, and it does not sign anything. CPA Canada’s guidance is blunt on this point: Copilot can increase efficiency, but it does not replace professional obligations, and firms need to build governance and human review into the workflow, not bolt it on afterward.

    That means every Copilot-assisted output needs a documented human checkpoint before it reaches a client or regulator. A workable structure: Copilot drafts, a senior accountant performs technical review and records acceptance or revision, and only the licensed professional’s final signature makes it a deliverable. Automate the repeatable handoffs between those steps, never the approval itself.

    A governance checklist worth adopting before scaling past a pilot:

    • Tenant-level access controls that match each role’s actual data needs, not blanket access.
    • Data minimization: don’t feed client PII into prompts when a redacted extract will do.
    • A written retention policy for AI-assisted drafts and the prompts that generated them.
    • Client disclosure where AI assistance materially shaped a deliverable.
    • An audit trail linking each AI-assisted output to its human reviewer.

    One licensing note that matters more than firms expect: for anything touching client financial data, use organization-grade Copilot experiences with enterprise data protection, not personal or consumer versions. The difference isn’t marketing language. It determines whether your prompts and data stay inside your tenant’s compliance boundary.

    Getting Started: A Compact Adoption and ROI Playbook

    Most Copilot rollouts fail the same way: licenses get purchased, a training webinar happens, and adoption quietly plateaus. A telemetry-driven pilot avoids that trap by measuring instead of guessing.

    1. Pick one workflow. Reconciliation and AR collections are the two fastest wins, because their inputs are structured and their time cost is easy to measure.
    2. Baseline before you touch anything. Time the current process by hand for two weeks before introducing Copilot, so your ROI claim later has a real comparison point.
    3. Find the dormant licenses. Usage telemetry, not survey responses, tells you which of your existing Copilot seats are sitting idle, which is where most firms are already losing money.
    4. Map the workflow to specific Copilot actions, using the prompt recipes above as a starting template rather than building from scratch.
    5. Automate the handoffs Copilot doesn’t cover, using tools like n8n or Python scripts to move data between systems Copilot can’t reach directly.
    6. Measure and report. Track time saved per workflow, reduction in close-cycle days, and license utilization rate, then expand to the next workflow only once the first shows a measurable result.

    Pro Tip: Track “recovered billable time,” not just “time saved.” A partner who reclaims four hours a week only creates value if that time gets rebilled or reinvested in client work, not absorbed into longer lunch breaks.

    and belong here once your pilot completes, because a specific before-and-after number does more to win partner buy-in than any vendor pitch deck.

    What We’ve Learned Rolling Out Copilot at Mid-Market Firms

    The biggest blocker isn’t the AI. It’s undocumented spreadsheets built by one person who left three years ago, and firms that skip telemetry never find out which licenses are actually idle. Reconciliation and AR collections deliver the fastest wins, but governance has to come before scale, not after.

    — Mad

    How Zera Helps Firms Turn Copilot Licenses Into Billable Hours

    Gozera exists for the exact gap most firms hit after go-live: licenses purchased, adoption stalled, and no clear number to show for the spend. We start with telemetry to find which Copilot seats sit unused, then run focused workflow sprints, reconciliation, AR collections, document review, mapped to the prompt patterns covered above and automated where needed with Python and n8n.

    Gozera

    An initial engagement gets you three concrete things: a usage baseline, a recommended pilot workflow chosen from your actual data, and an estimated ROI figure your managing partners can evaluate before committing further. If your firm has more Copilot seats than active users, that’s the signal worth acting on. Book an audit with Zera to see where your licenses are actually going.

    Sources